CodeSign Secure Documentation
  • Overview
    • About CodeSign Secure
    • Getting Started
    • Documentation Guide
    • Portal Overview
    • Troubleshooting
      • FAQ
    • Glossary
  • Reference Guide
    • Header Bar
      • CodeSign Secure Documentation
      • Swagger API
      • Profile Section
    • Dashboard
      • Key Performance Indicators
      • Issued Certificates
      • Signatures Generated
      • HSM Health Check
    • Keys and Certificates
      • Key and Certificate Lifecycle
    • App Management
    • Signing Requests
      • Approval Workflows
    • Signing Tools
    • Reports
      • Signing Request Report
      • Audit Trail
      • Certificate Report
      • Client Report
    • Logs
    • System Setup
      • Identity Store
      • Backup
      • User
      • Roles and Permissions
      • Email
      • Signing Projects
      • SSL/TLS Management
      • Environment
      • Plugins
  • Setup & Architecture
    • Identity and Access Control
    • Architecture and Concepts
    • Installation
      • Windows
        • Installing the Server
        • Ports and Protocols
        • High Availability and Backup
        • Upgrades and Compatibility
    • Security
      • Security Hardening Checklist
      • Client Authentication
      • Designing Signing Policies
  • Release Notes
    • Releases for 2026
      • v3.2.1
    • Releases for 2025
      • v3.2.0
    • Releases for 2024
      • v3.1.0
  • API Reference
    • Getting Started
    • Authorizing Requests
    • Securing API Access
    • Request and Response Conventions
    • Endpoint Reference
      • Signing
      • Signing Requests
      • Certificates
      • Applications and Environments
      • User Management
      • Permissions
      • Email
      • System Setup
      • Reports
      • Dashboard
      • License
  • Integration Guides
    • Signing Capabilities
      • Supported Formats and Platforms
      • Timestamping
      • Windows Signing - SignTool
        • Signing
        • Macro Signing
      • Apple Signing
      • AppX & MSIX Signing
      • Visual Studio ClickOnce
      • Jar Signing
      • Sign HLK/HCK using CodeSign Secure
      • NuGet Signing
      • Mage Signing
      • Sign OVA/OVF using Encryption Consulting’s Utility Tool
      • Utility Tool for code signing
      • Container Signing
      • PKCS11 Wrapper
        • APK Signing
        • OpenSSL Signing
        • XML Signing
        • JSign Tool Signing
        • Jarsigner Signing
        • GPG2, Debian & RPM Signing
      • Reproducible Build
        • Automated Hash Validation
        • Reproducible Build Process Flow
        • Pipeline Script Components
        • Hash Validation
    • CI/CD Integration
      • GitHub Actions
      • Jenkins
      • GitLab
      • Azure DevOps
      • TeamCity
      • Bamboo
      • Securing CI/CD Credentials

SSL/TLS Management

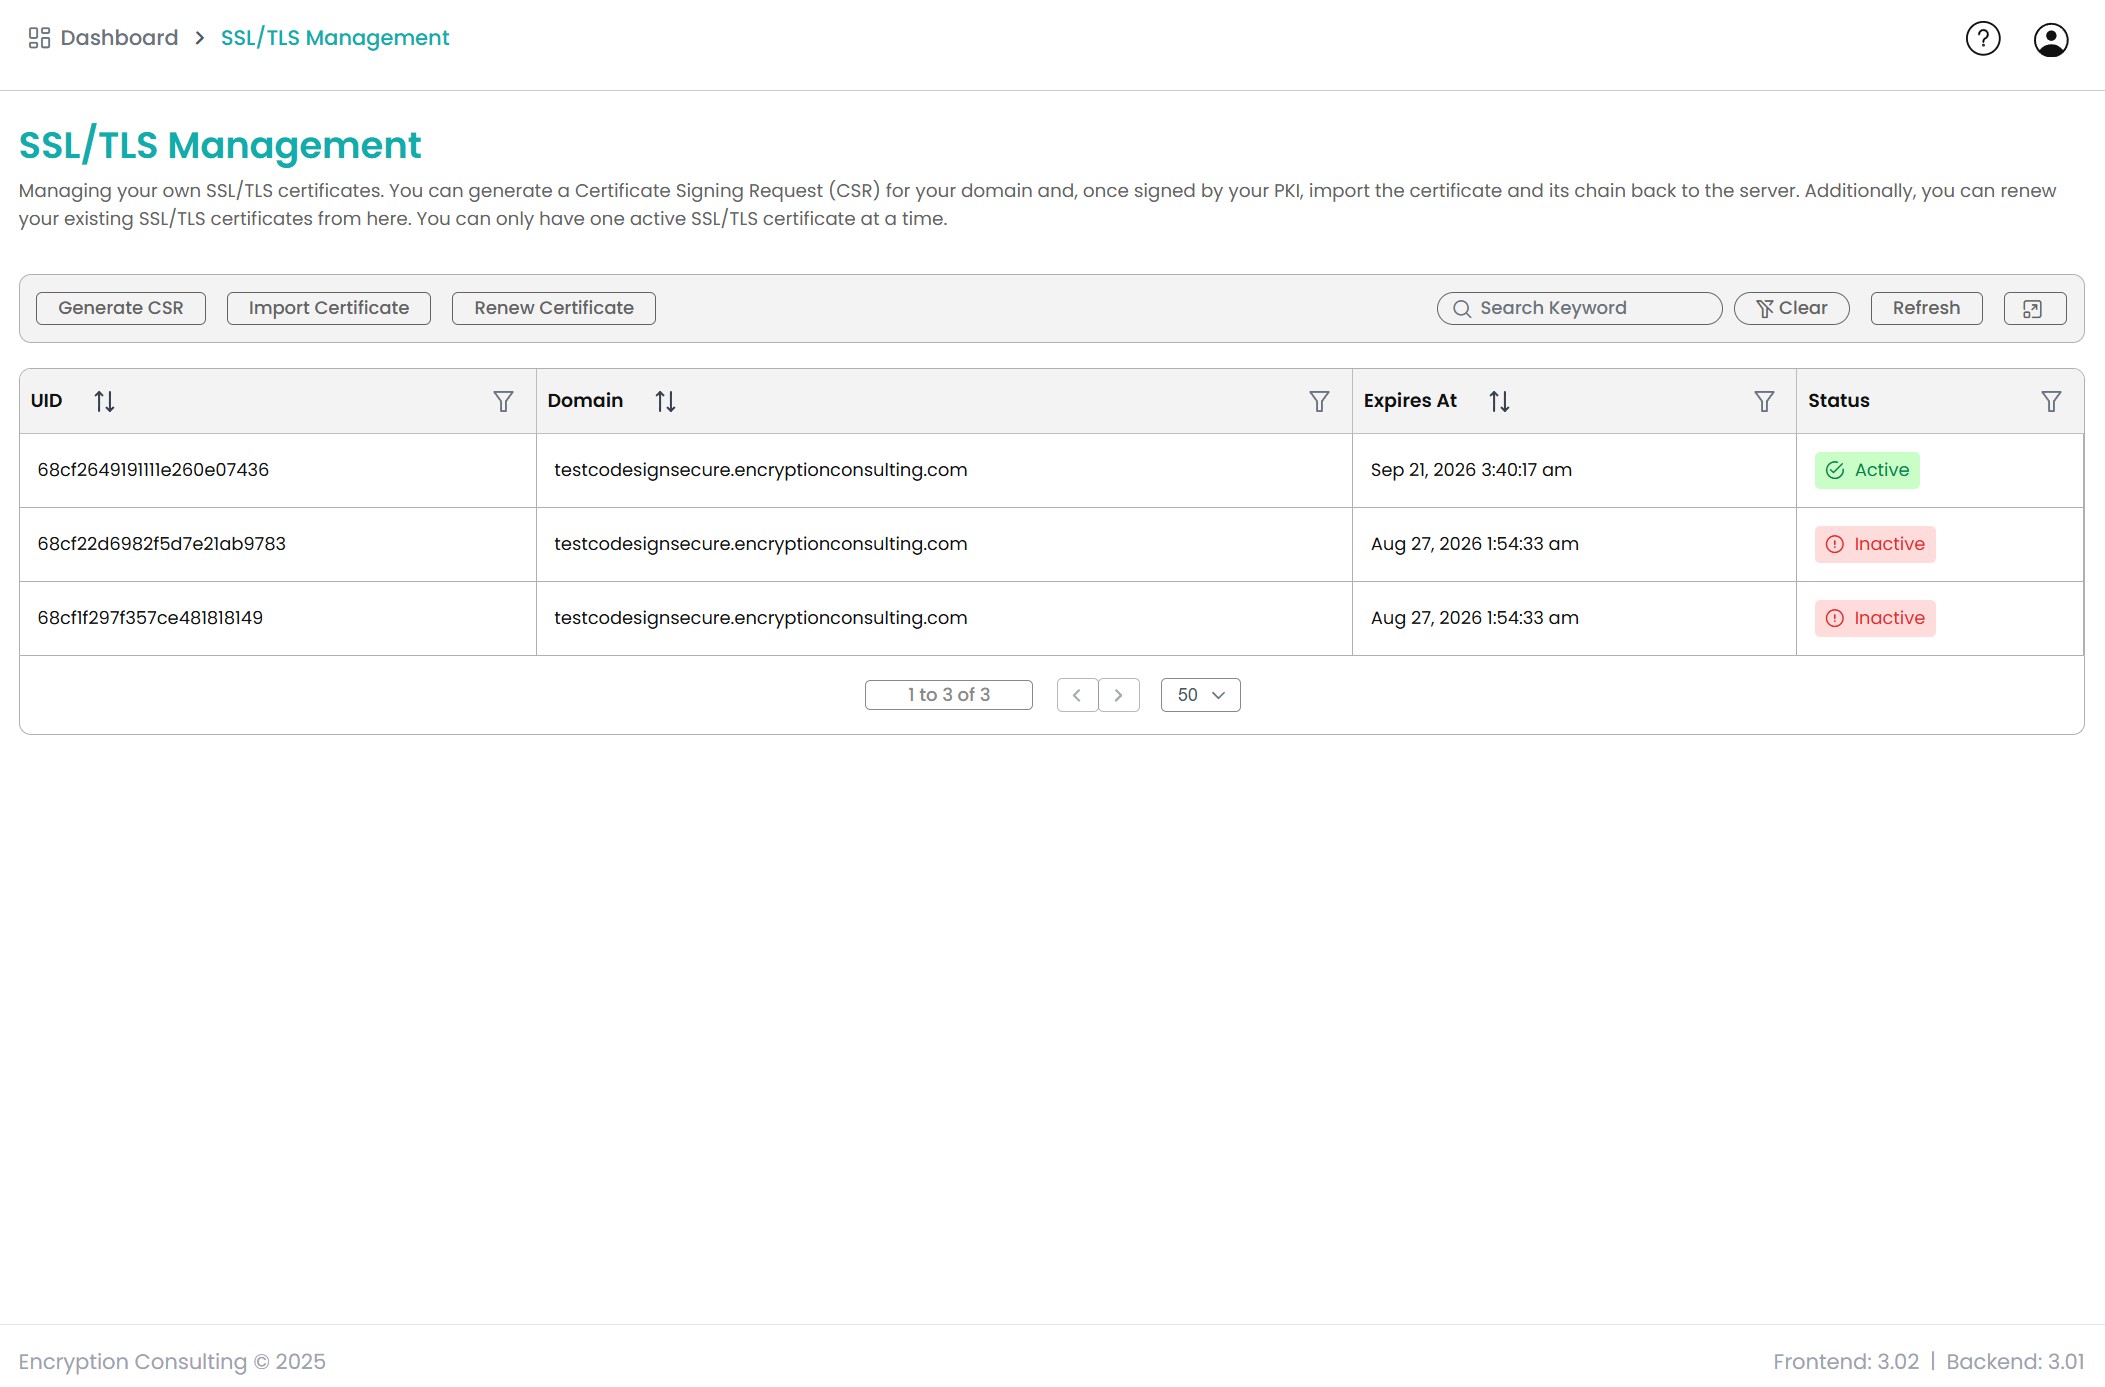
This page allows you to manage your SSL/TLS certificates signed via your external PKI.

SSL/TLS Management Section

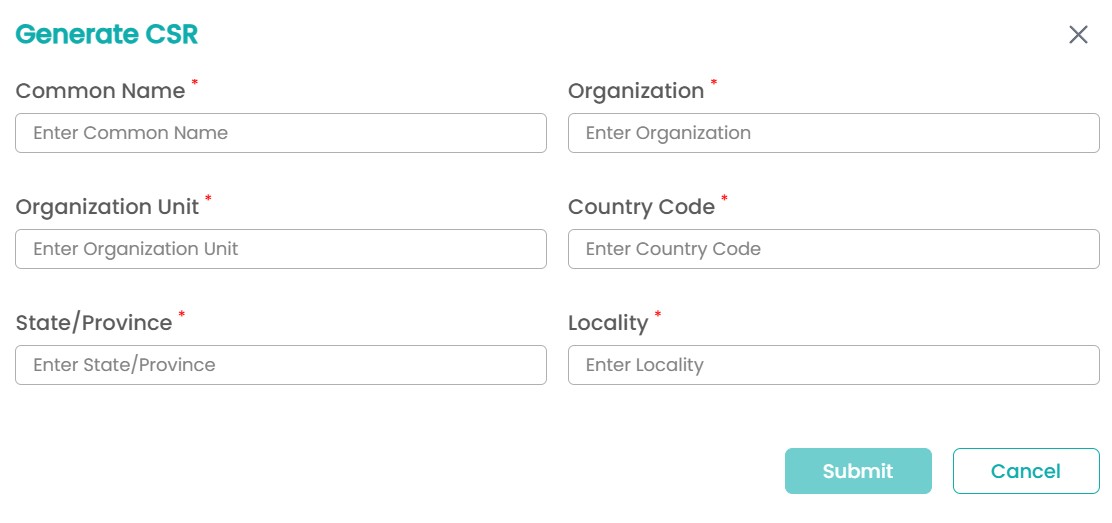
To set your own SSL/TLS certificate, you can generate Certificate Signing Request (CSR) for your domain. Common name for SSL/TLS certificate should be the domain name of the portal like codesign.example.com.

Generate CSR Section

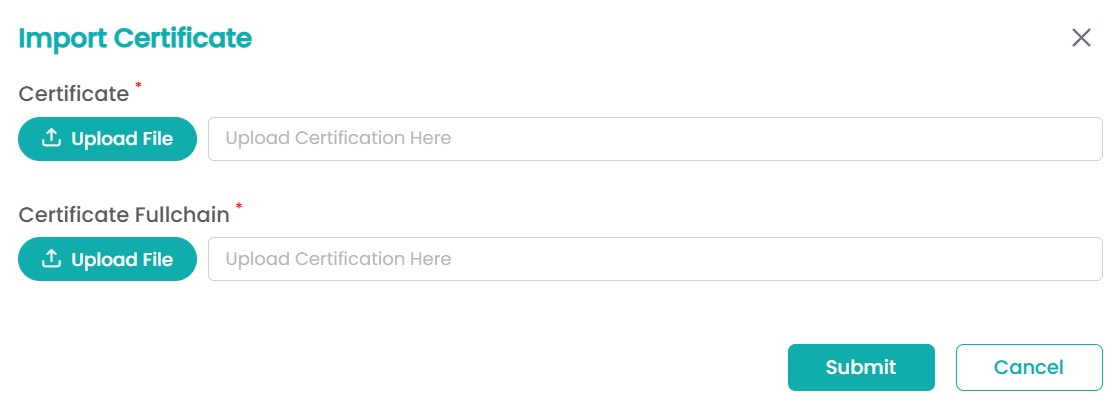
Once signed by your PKI, import the certificate and its full chain back to the server.

Import Certificate Section

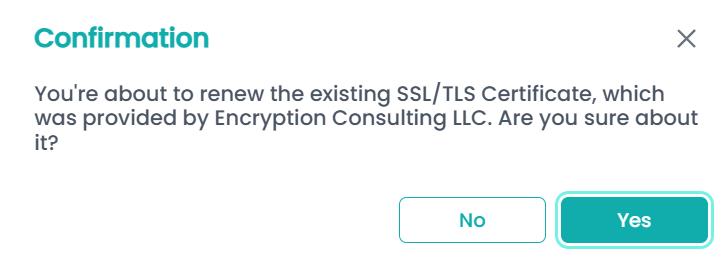
Additionally, you can renew the active SSL/TLS certificate if it is the self-signed certificate provided with CodeSign Secure. Certificates issued through a CSR and imported can’t be renewed; before one expires, generate a new CSR and import the new certificate.

Note: Renew is available only for the active self-signed SSL/TLS certificate provided with CodeSign Secure, not for certificates issued through a CSR and imported.

Certificate Renew Confirmation
On this Page:
Support Privacy Policy Terms of Service

Copyright Encryption Consulting LLC. All rights reserved.