Open SSL Signing
Let's see how to perform OpenSSL-based signing using CodeSign Secure and Encryption Consulting’s
PKCS#11 wrapper on both Ubuntu and Windows, covering setup, configuration, and execution. Whether you’re
working in enterprise environments or building a secure signing process for your app, this setup will help
you strengthen your cryptographic hygiene without a steep learning curve.
For Linux - Ubuntu
Installation on Client System
-
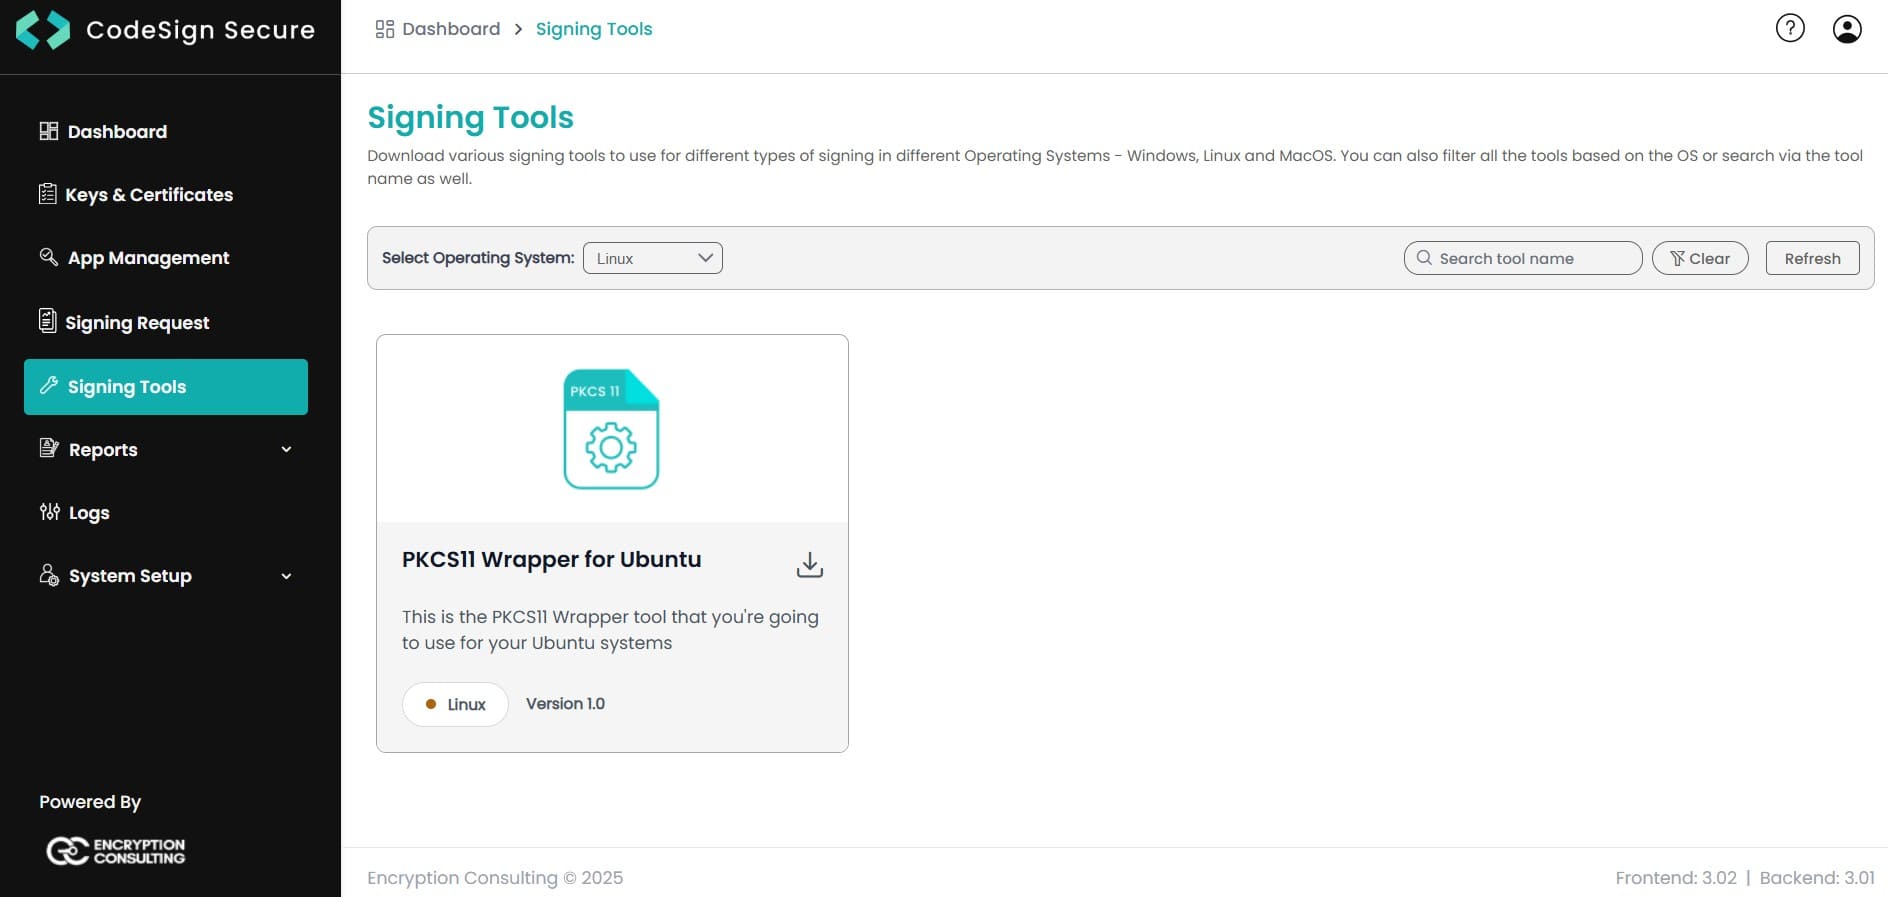
Go to EC CodeSign Secure’s v3.02 Signing Tools section and
download the PKCS11 Wrapper for Ubuntu.
-
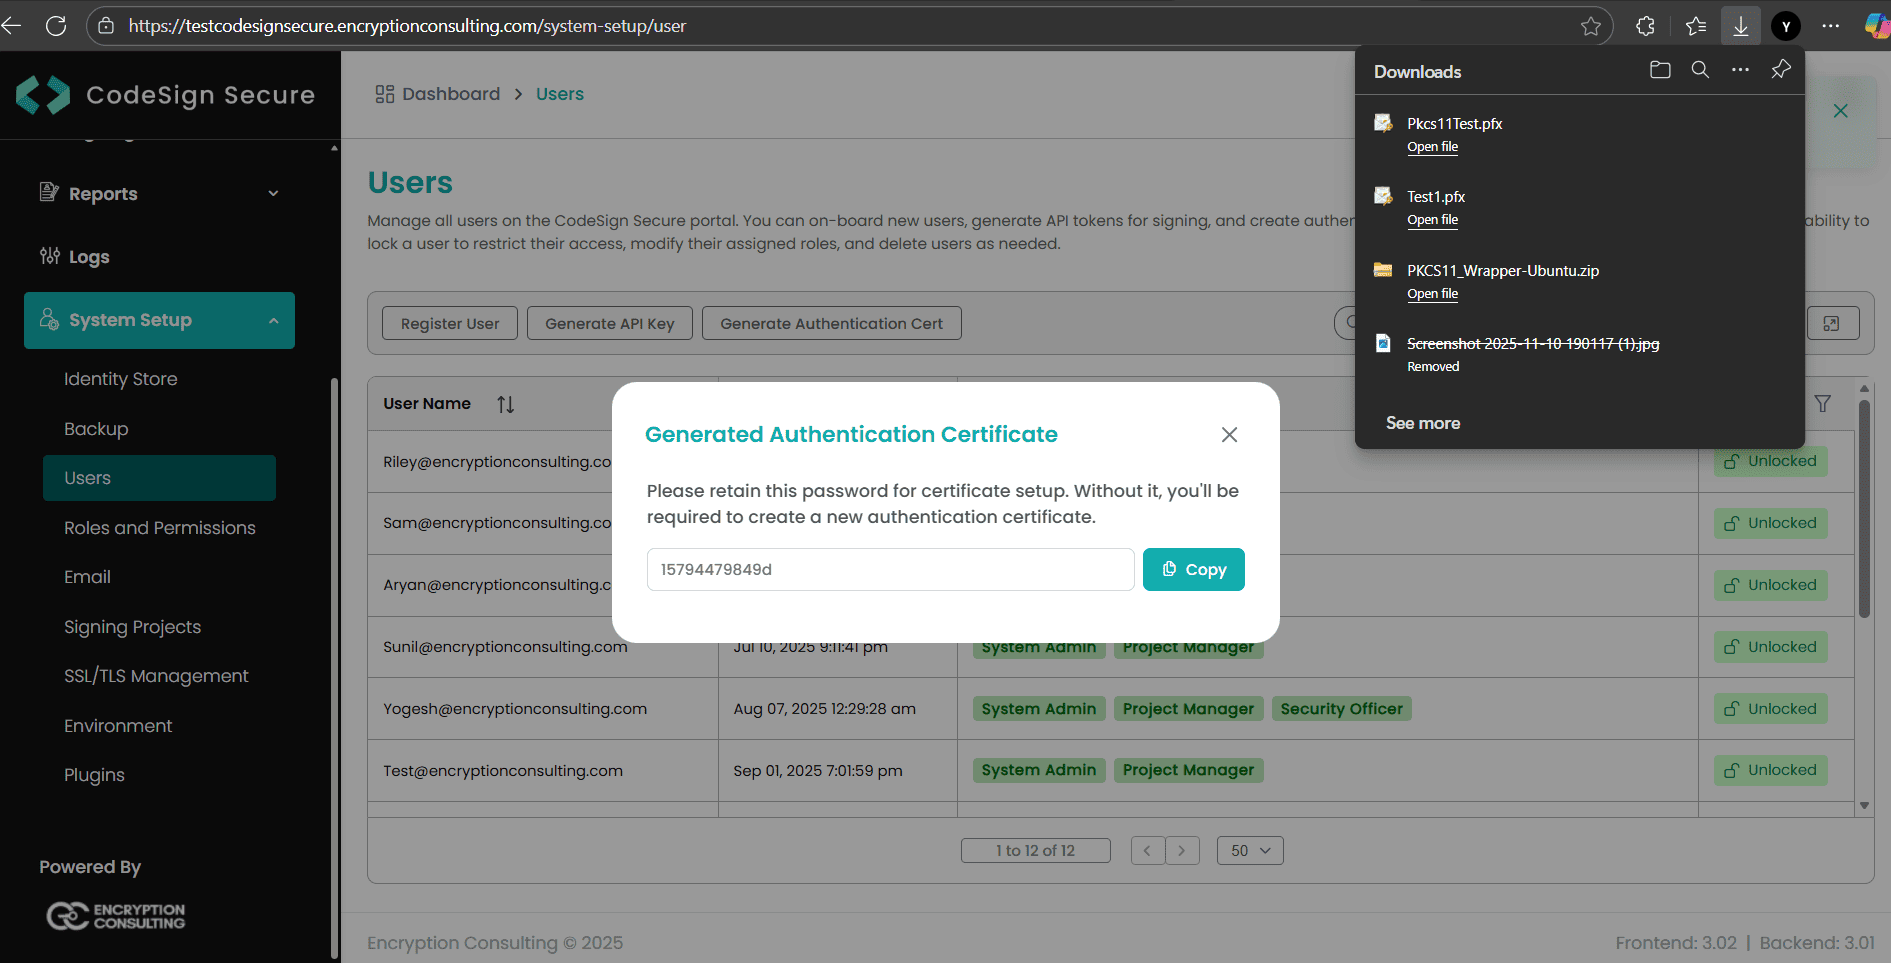
After that, generate a P12 Authentication certificate from the
System Setup > User > Generate Authentication
Certificate
dropdown.
-
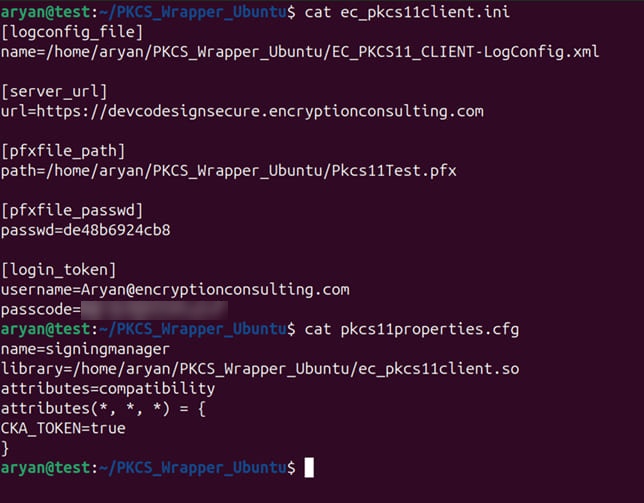
Go to your Ubuntu client system and edit the configuration
files (ec_pkcs11client.ini
and pkcs11properties.cfg)
downloaded in the PKCS11 Wrapper.
Prerequisites for the Ubuntu System
Now, let’s install some prerequisites in your client system to run the PKCS11 Wrapper.
-
Install OpenSSL: sudo apt install -y openssl libengine-pkcs11-openssl
gnutls-bin xxd
- Create a config file for PKCS#11
-
Enter the appropriate details in the config file:
openssl_conf = openssl_init
[openssl_init]
engines =
engine_section
[engine_section]
pkcs11 = pkcs11_section
[pkcs11_section]
#Path to the OpenSSL PKCS11 Engine
dynamic_path = "<Path to libpkcs11.so>"
MODULE_PATH = "<Path to ec_pkcs11client.so>"
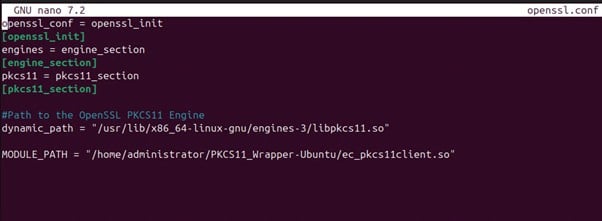
The ec_pkcs11client.so path depends on where you store the file.
The libpkcs11.so path depends on your Linux distribution and version:
- Ubuntu 18.04: /usr/lib/x86_64-linux-gnu/engines-1.1/libpkcs11.so
- Ubuntu 20.04: /usr/lib/x86_64-linux-gnu/engines-1.1/libpkcs11.so
- Ubuntu 22.04: /usr/lib/x86_64-linux-gnu/engines-3/libpkcs11.so
-
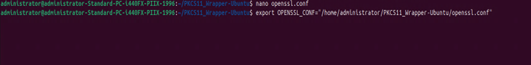
Set the environment variable for openssl.cnf file
export OPENSSL_CONF=<path to openssl.cnf>
Perform Signing and Verification using PKCS11 Wrapper
Now that all the configurations and prerequisites have been installed. Let’s perform the signing operation
first.
The signing command will look something like this (ensure you run this command only inside the
folder where
your PKCS11 Wrapper is installed):
openssl pkeyutl -engine pkcs11 -sign -in <path of the file you want to sign> -inkey
"pkcs11:object=<private key alias>;type=private" -keyform engine -out <path of the Signed file>
For Example:
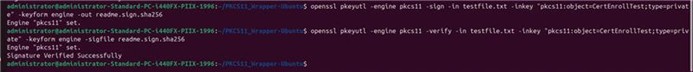
openssl pkeyutl -engine pkcs11 -sign -in testfile.txt -inkey "pkcs11:object=CertEnrollTest;type=private"
-keyform engine -out readme.sign.sha256
After successfully signing the file, let’s verify it using this command:
openssl pkeyutl -engine pkcs11 -verify -in <path of the file you want to sign> -inkey
"pkcs11:object=<private key alias>;type=public" -keyform engine -sigfile <path of the Signed file>
For Example:
openssl pkeyutl -engine pkcs11 -verify -in testfile.txt -inkey "pkcs11:object=CertEnrollTest;type=public"
-keyform engine -sigfile readme.sign.sha256
For Windows
Installation on Client System
-
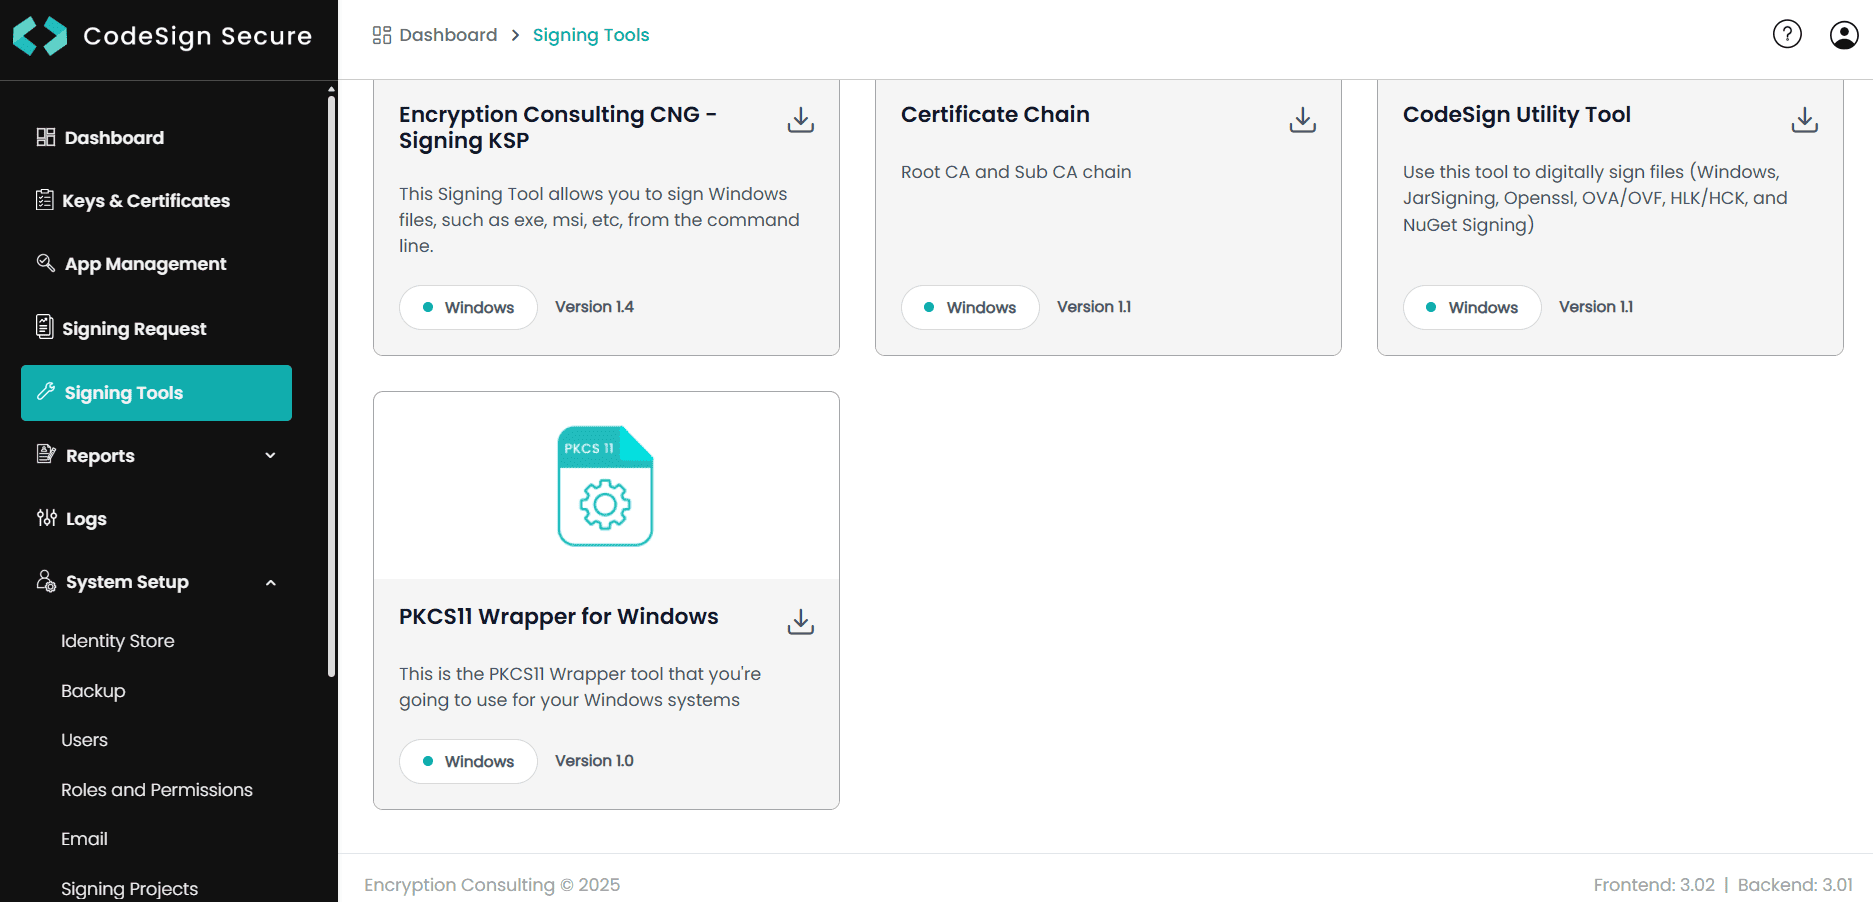
Go to EC CodeSign Secure’s v3.02 Signing Tools section and download the PKCS11 Wrapper for Windows.
-
After that, generate a P12 Authentication certificate from the
System Setup > User > Generate Authentication
Certificate
dropdown.
-
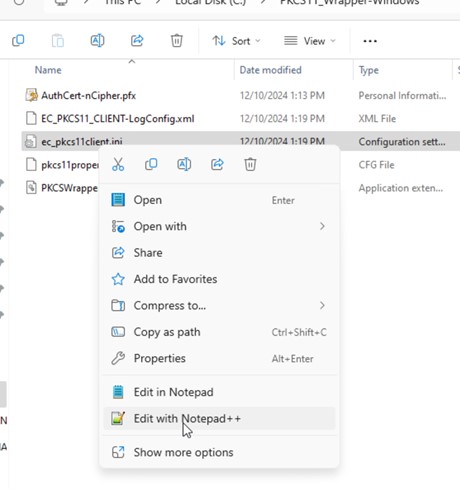
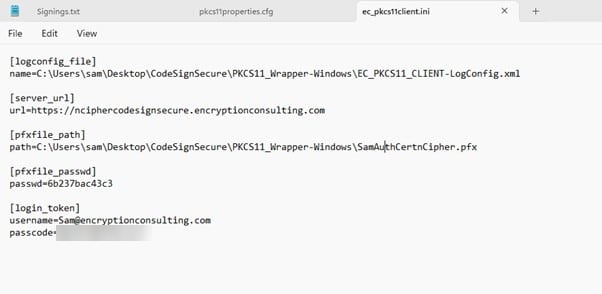
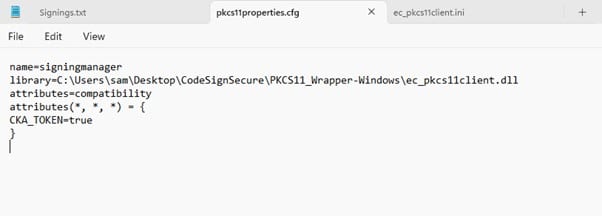
Go to your Windows client system and edit the configuration
files (ec_pkcs11client.ini
and pkcs11properties.cfg)
downloaded in the PKCS11 Wrapper.
Prerequisites for Windows System
Now, let’s install some prerequisites in your client system to run the PKCS11 Wrapper.
-
Download and install OpenSSL on your system from here.
-
Manually compile the OpenSSL PKCS#11 using these methods
- Download and install msys2-i686-*.exe from here
- Start a MSYS2 MSYS console from the Start menu
Use this command:
pacman -S git pkg-config libtool autoconf automake make gcc openssl-devel
git clone https://github.com/OpenSC/libp11.git
cd libp11
autoreconf -fi
./configure --prefix=/usr/local
make && make install
-
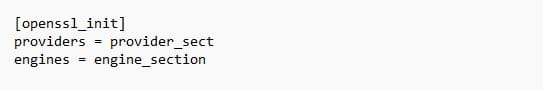
In the configuration file (openssl.cnf) in the folder C:\Program Files\Common Files\SSL
Add these lines:
openssl_conf = openssl_init
[openssl_init]
engines =
engine_section
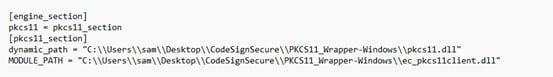
[engine_section]
pkcs11 = pkcs11_section
[pkcs11_section]
#Path to the Compiled OpenSSL PKCS11 from OpenSC - libp11
dynamic_path = <Path to compiled libp11 pkcs11.dll>
MODULE_PATH = <Path to ec_pkcs11client.dll>
Perform Signing and Verification using PKCS11 Wrapper
Now that all the configurations and prerequisites have been installed. Let’s perform the signing
operation
first.
The signing command will look something like this (ensure you run this command only inside
the folder where
your PKCS11 Wrapper is installed):
openssl dgst -engine pkcs11 -keyform engine -sign "pkcs11:object=<private key alias>;type=private"
-sha256 -out <path of signed file> <path of file to sign>
For Example:
openssl dgst -engine pkcs11 -keyform engine -sign "pkcs11:object=CertEnrollTest;type=private" -sha256 -out
test-signed.bin testfile.txt
After successfully signing the file, let’s verify it using this command:
openssl dgst -engine pkcs11 -keyform engine -verify "pkcs11:object=<private key alias>;type=public"
-sha256 -signature <path of signed file> <path of file to sign>
For Example:
openssl dgst -engine pkcs11 -keyform engine -verify "pkcs11:object=CertEnrollTest;type=public" -sha256
-signature test-signed.bin testfile.txt
Security Considerations
When you’re dealing with cryptographic operations—especially digital signing—the protection of your private
keys is absolutely non-negotiable. A leaked or compromised private key is pretty much a worst-case scenario
because it opens the door to impersonation, unauthorized access, and a whole lot of trust issues.
- Never store private keys in plain files: It might be convenient,
but storing private keys as flat files on disk (even with file system permissions) is risky. All it takes
is a misconfigured backup system or a curious admin to accidentally expose them. Instead, use secure key
storage mechanisms—preferably hardware-backed.
- Use HSMs or secure tokens whenever possible: Hardware Security
Modules (HSMs) and smart cards are built specifically for secure key storage. They don’t just store
keys—they perform operations (like signing or decryption) inside the device, so the private key never
actually leaves. This adds a strong layer of protection, especially against malware or insider threats.
- Lock down access to your PKCS#11 modules: Make sure only authorized
users or services can talk to the PKCS#11 interface. Use PINs, role-based access, and proper auditing to
prevent abuse. If your wrapper or HSM vendor supports logging, enable it—you’ll want a clear trail of who
accessed what and when.
- Avoid leaving tokens unlocked: It’s tempting to script things and
leave tokens unlocked to “keep things running,” but that’s risky. Instead, look into automated unlock
mechanisms that still respect session isolation or tools that securely cache credentials for short
durations with tight access controls.
- Validate what you’re signing: It sounds obvious, but make sure
you’re not signing random or malicious files by accident. Build in sanity checks or use pre-signing
verification steps to ensure only approved content goes through your signing flow.
