Azure Devops
-
Navigate to dev.azure.com and sign in with your Microsoft
account or you can start free with your GitHub Account too
-
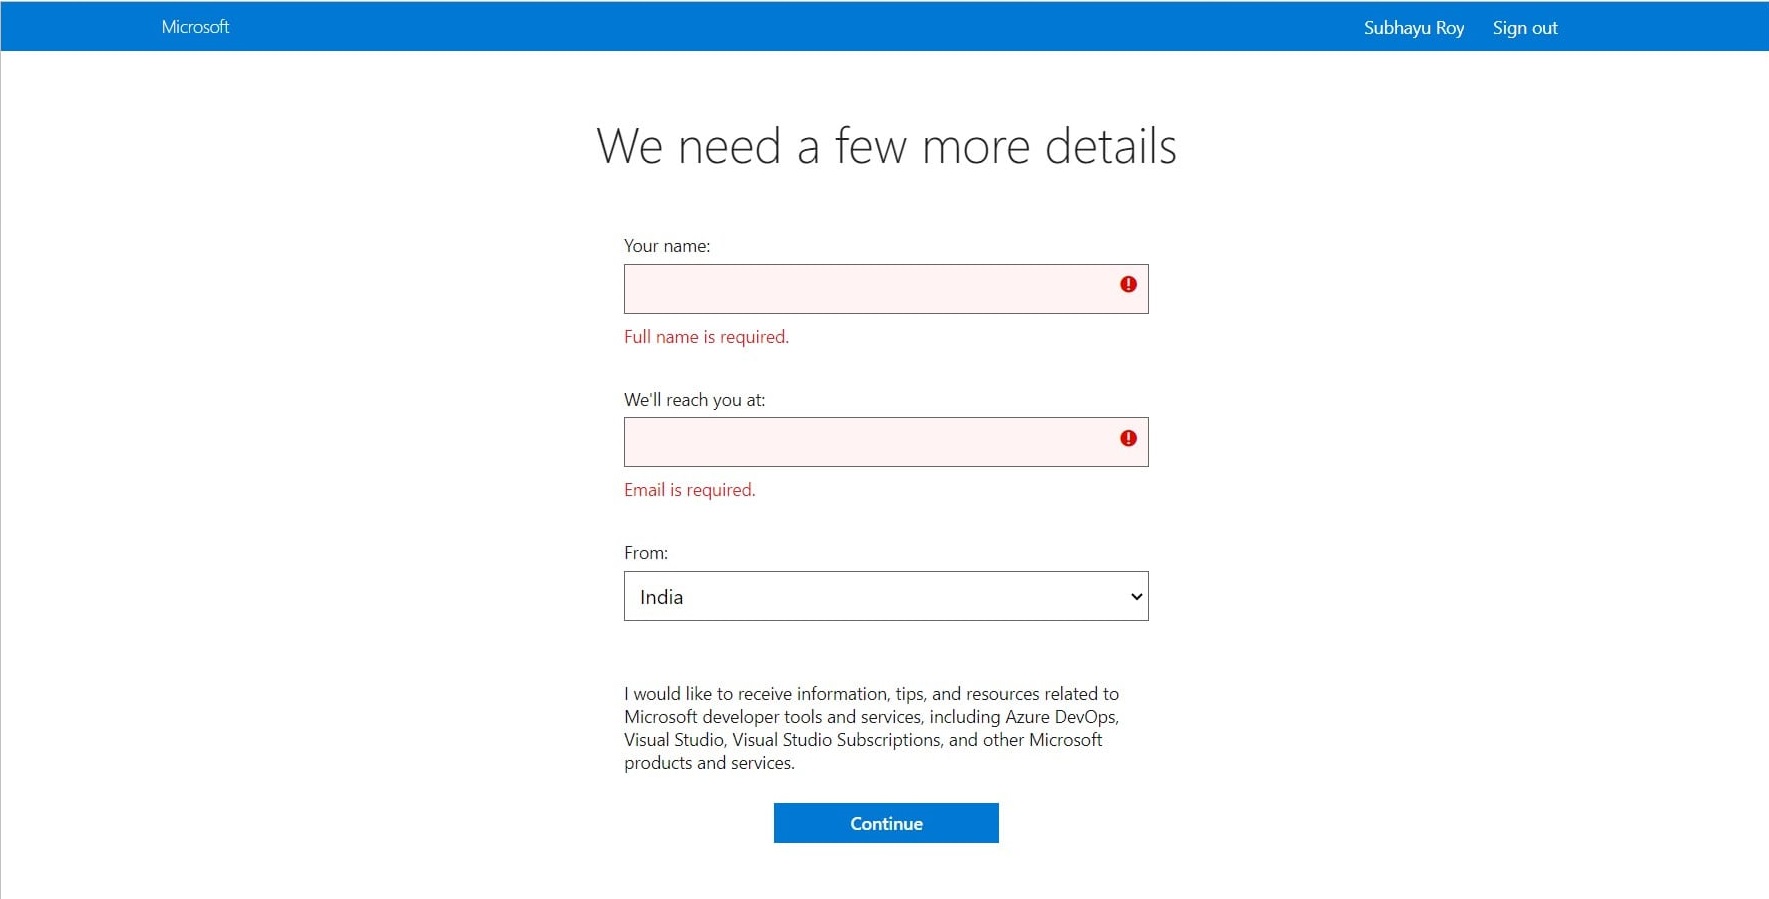
Give the details as prompted
-
You’ll be asked to create an organization if you haven’t
already. Create a organization and get started with the project.
-
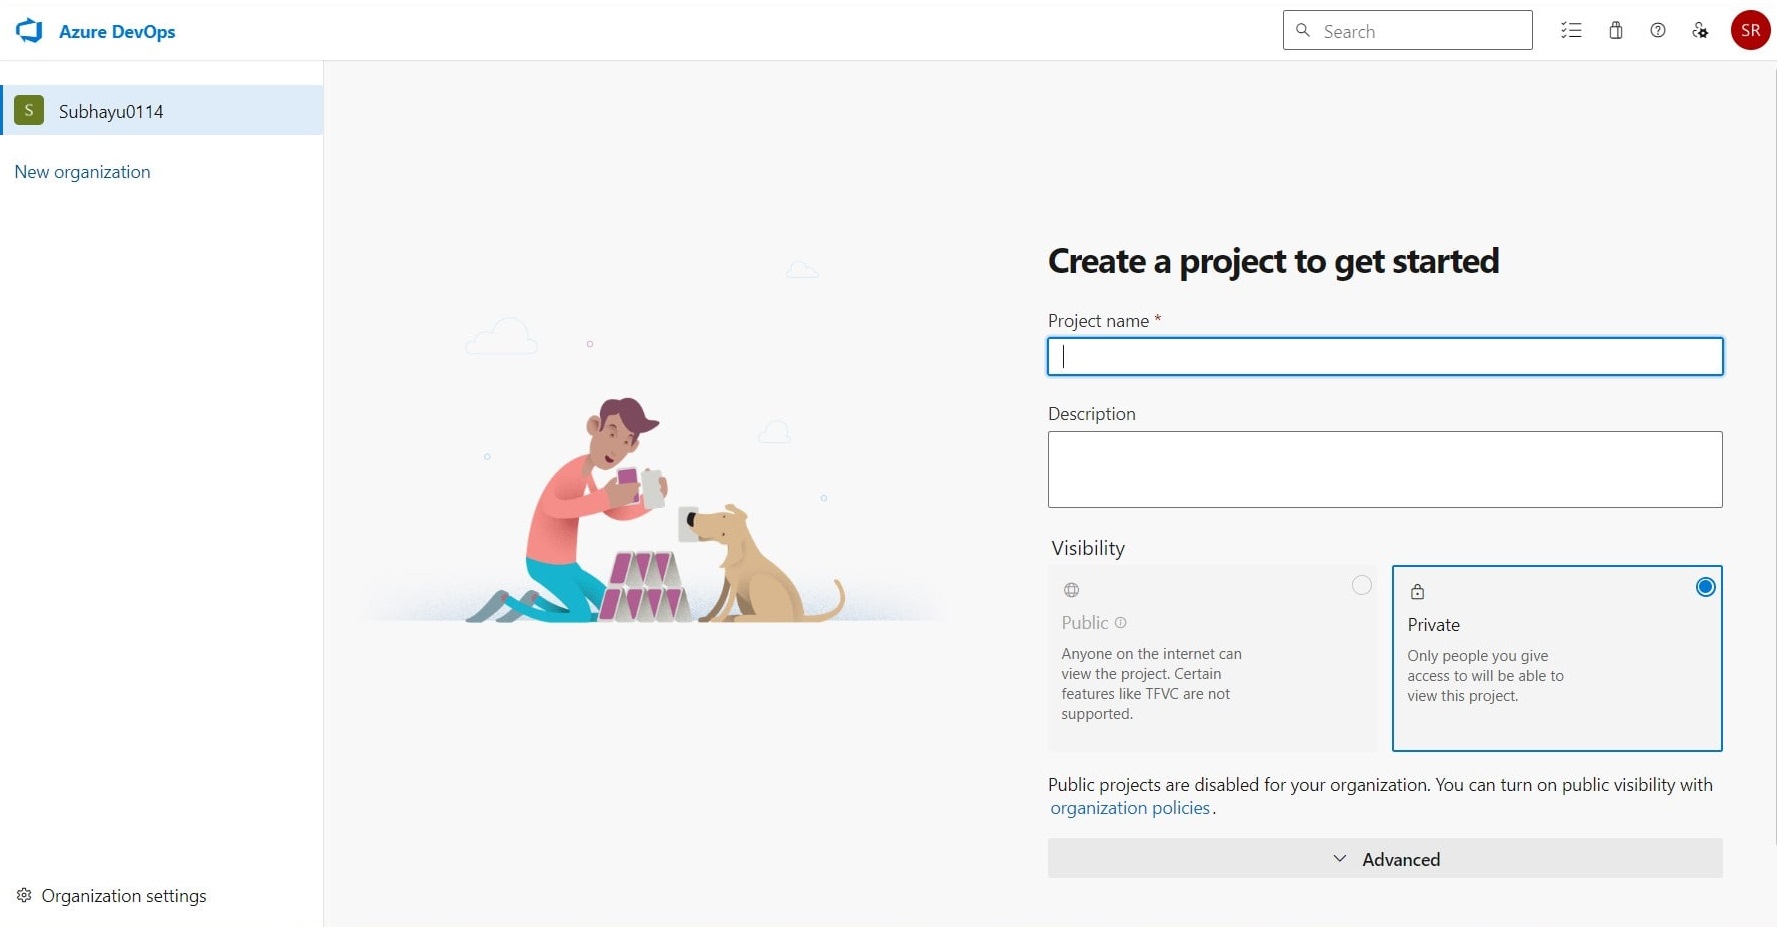
If you already have a project where you want to build the
pipeline, navigate to pipelines. If not create a simple
project first. Provide the necessary details to continue.
-
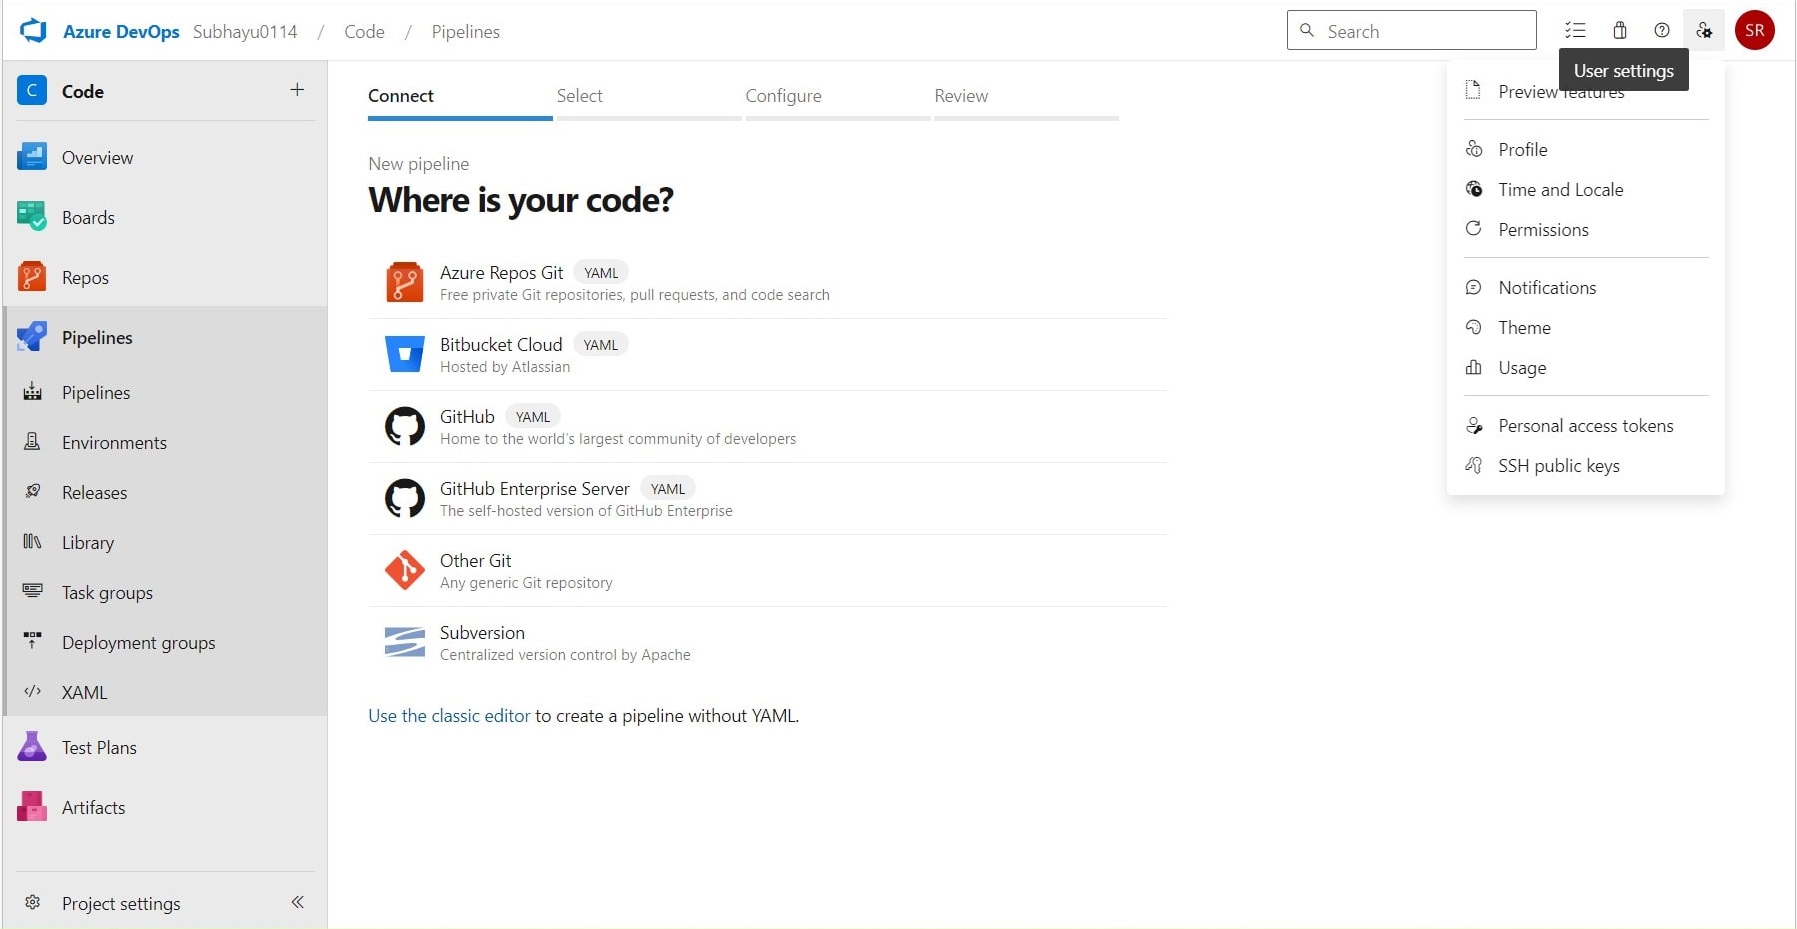
After a project is made, navigate to user setting at the top
left corner of your screen and click on personal Access token.
On the next page click on “New Token”. On the dialogue box
prompted, provide necessary details such as name of the token,
organization name (the organization you created/accessed
earlier. Set Expiration and Scopes. I have set the Scope to
full access.
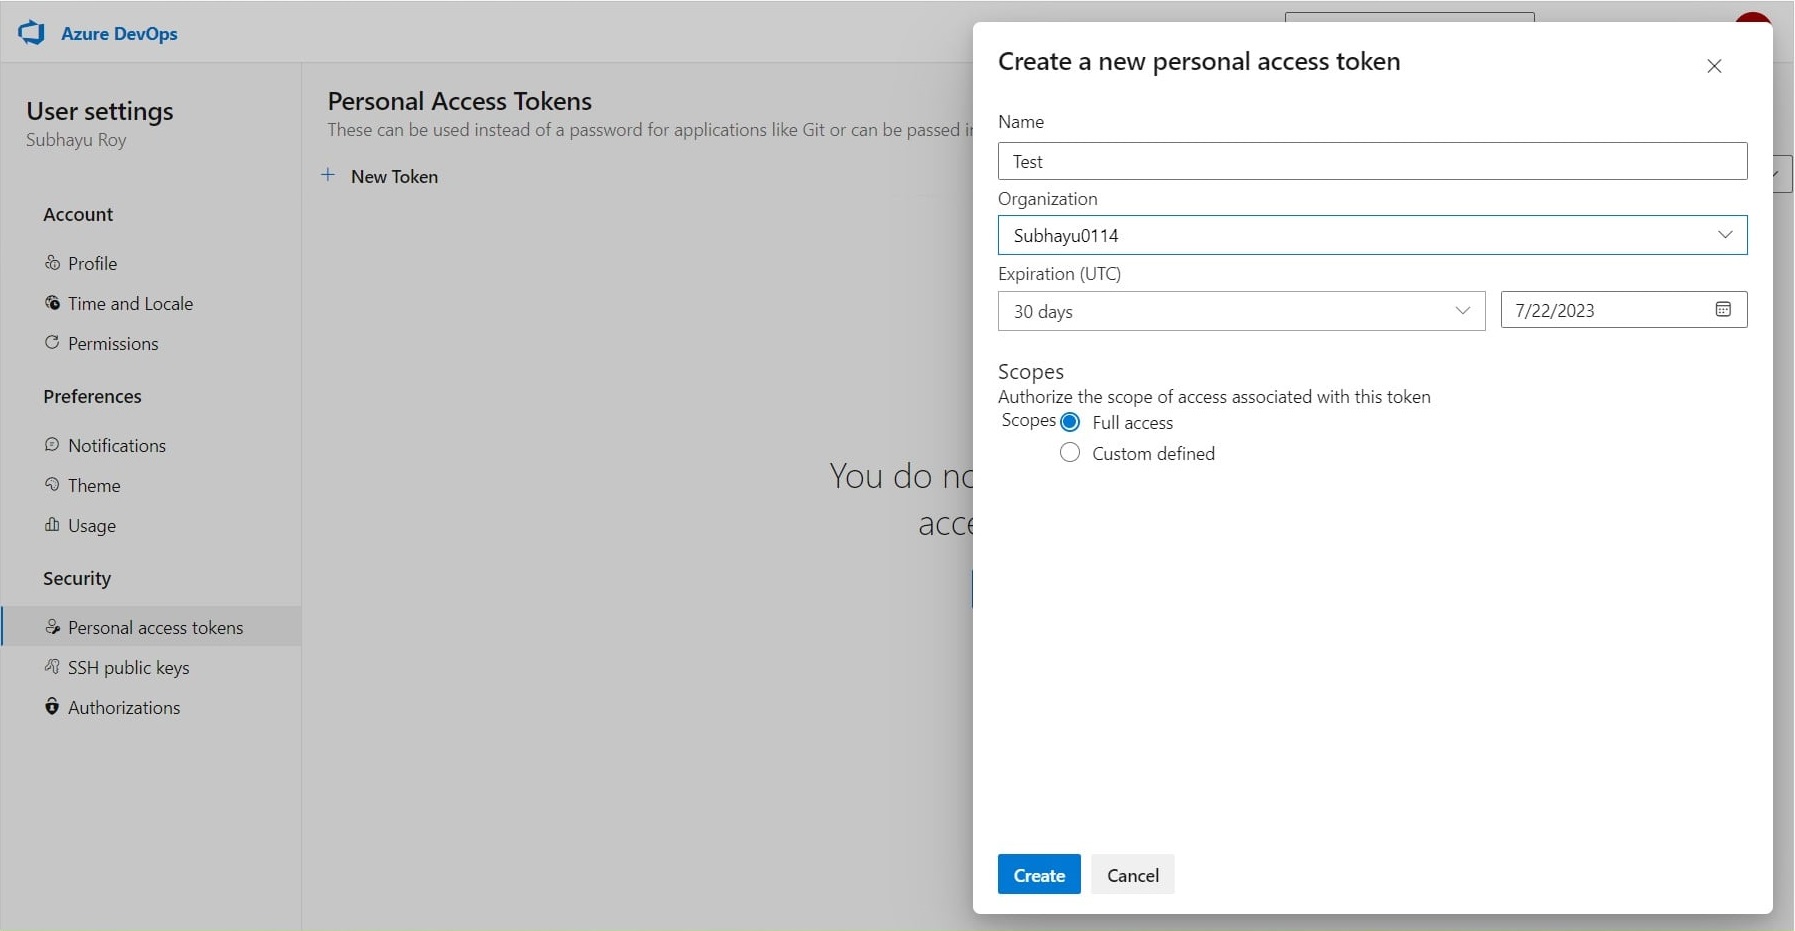
Click on create and copy the token somewhere as you won’t be
able to see the token again.
-
After we are done getting a token, we need to set up a
self-hosted runner. This is a machine where Signtool and
ECSigningKSP is installed and configured. To do so return to
the Code Summary page and on the bottom left of the screen
you’ll see Project settings, click on that.
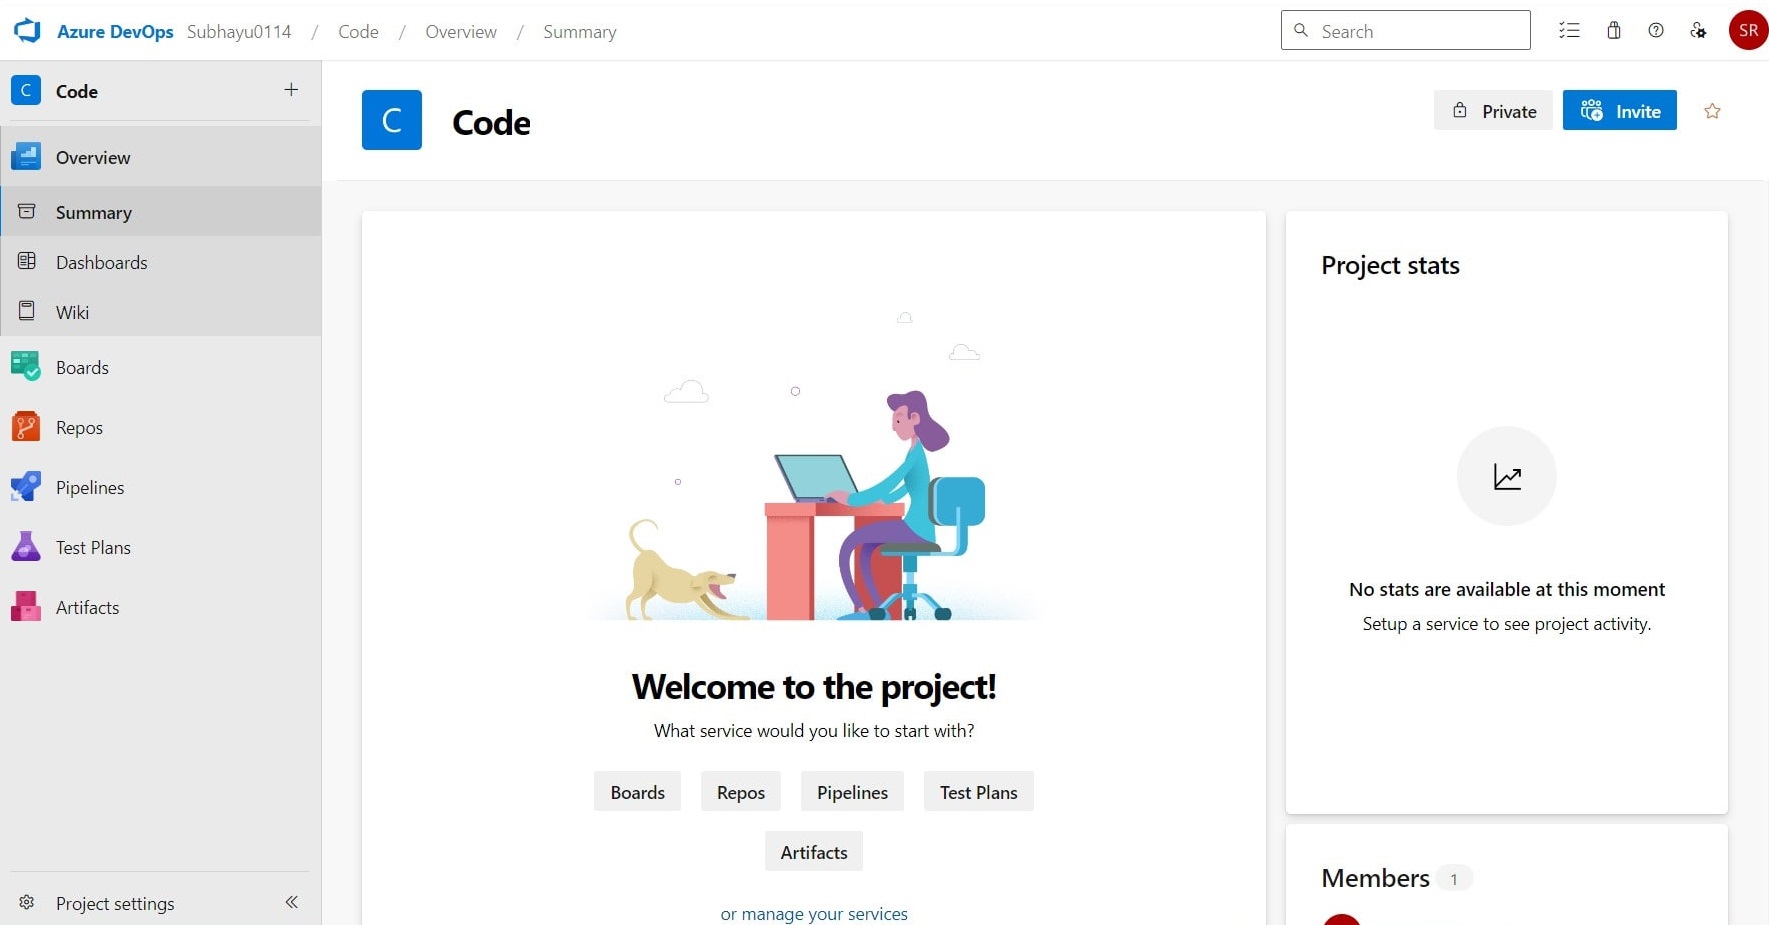
Under Pipelines, you’ll see Agent Pools. Click on that and
then click on default.
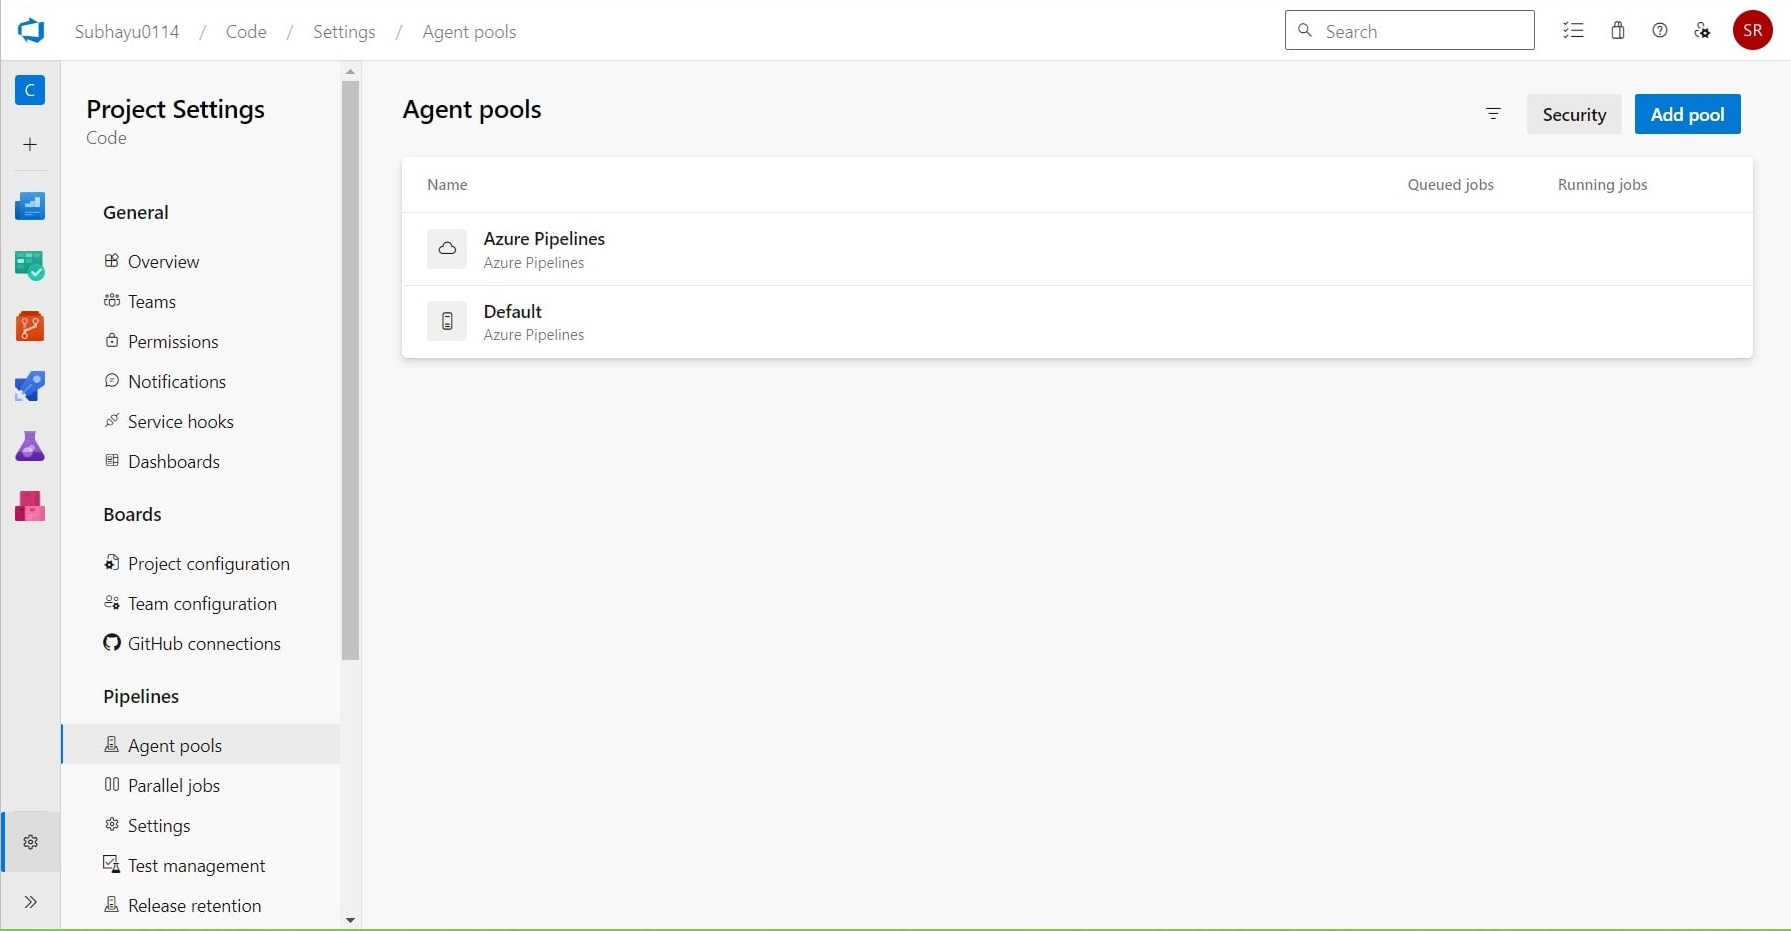
Click on new agent at the top left.
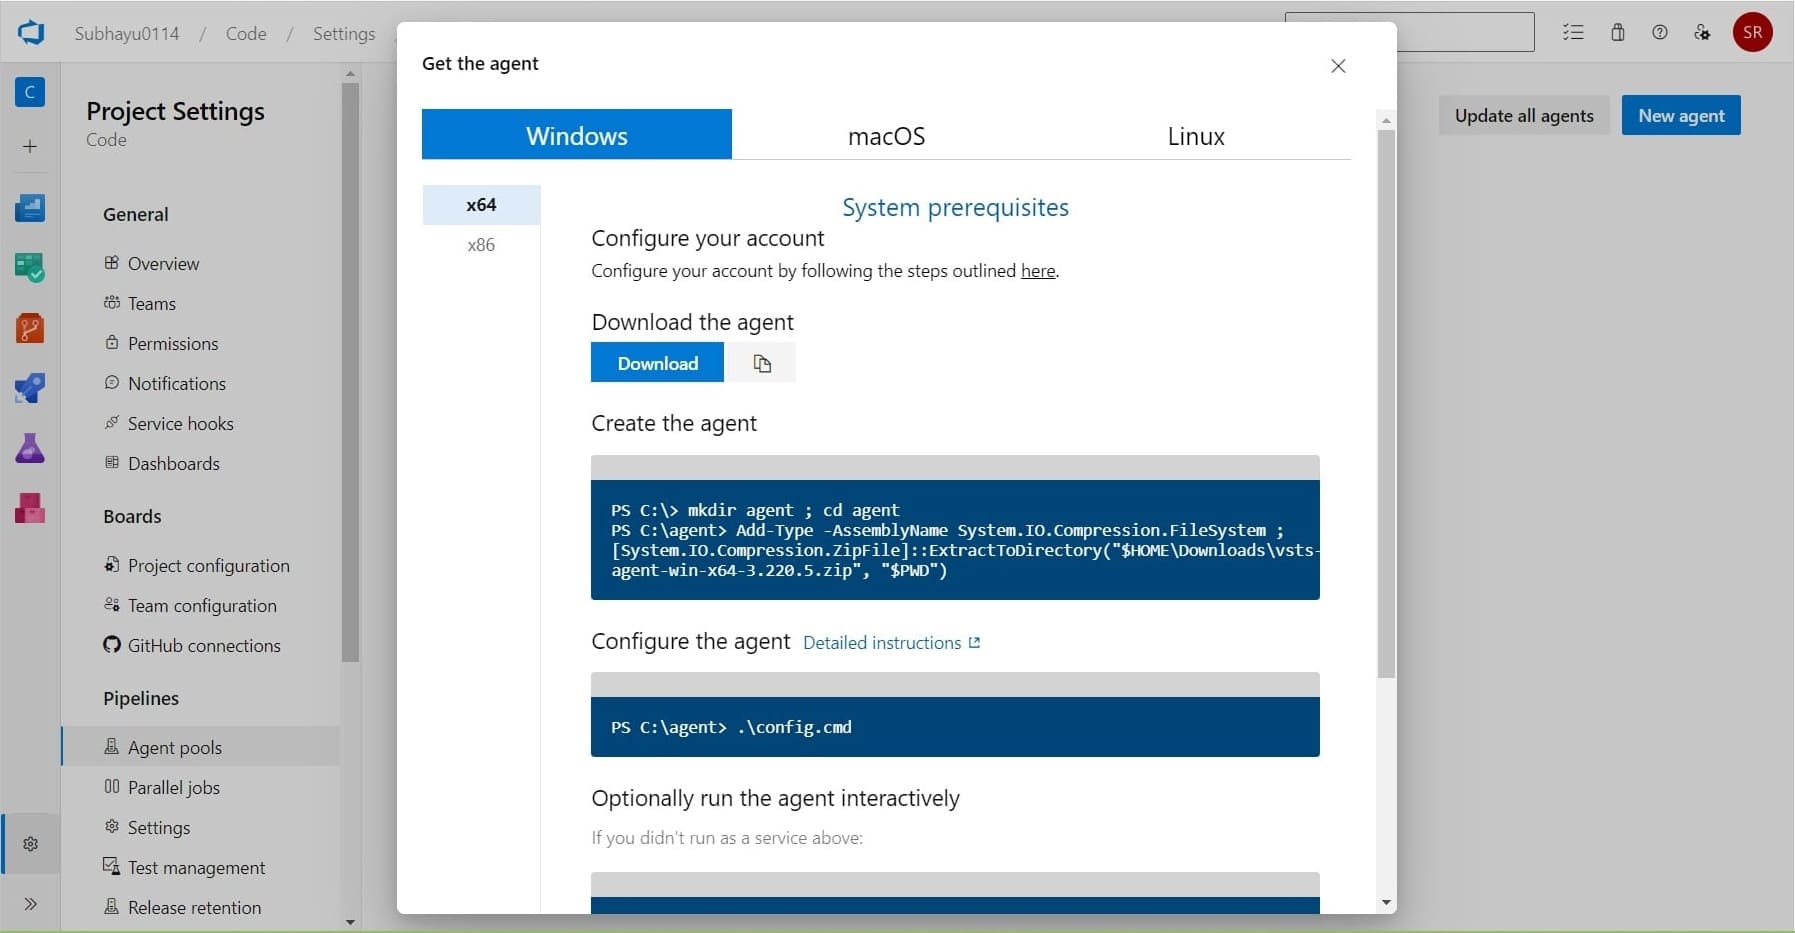
Get the agent as per your operating system. I am proceeding
with windows. Download the agent, extract it to a folder
“C:\agents”.
You can also follow this
documentation
for more help about this
-
After you extract the files, navigate to the folder where you
extracted it to from cmd and run .\config.cmd.
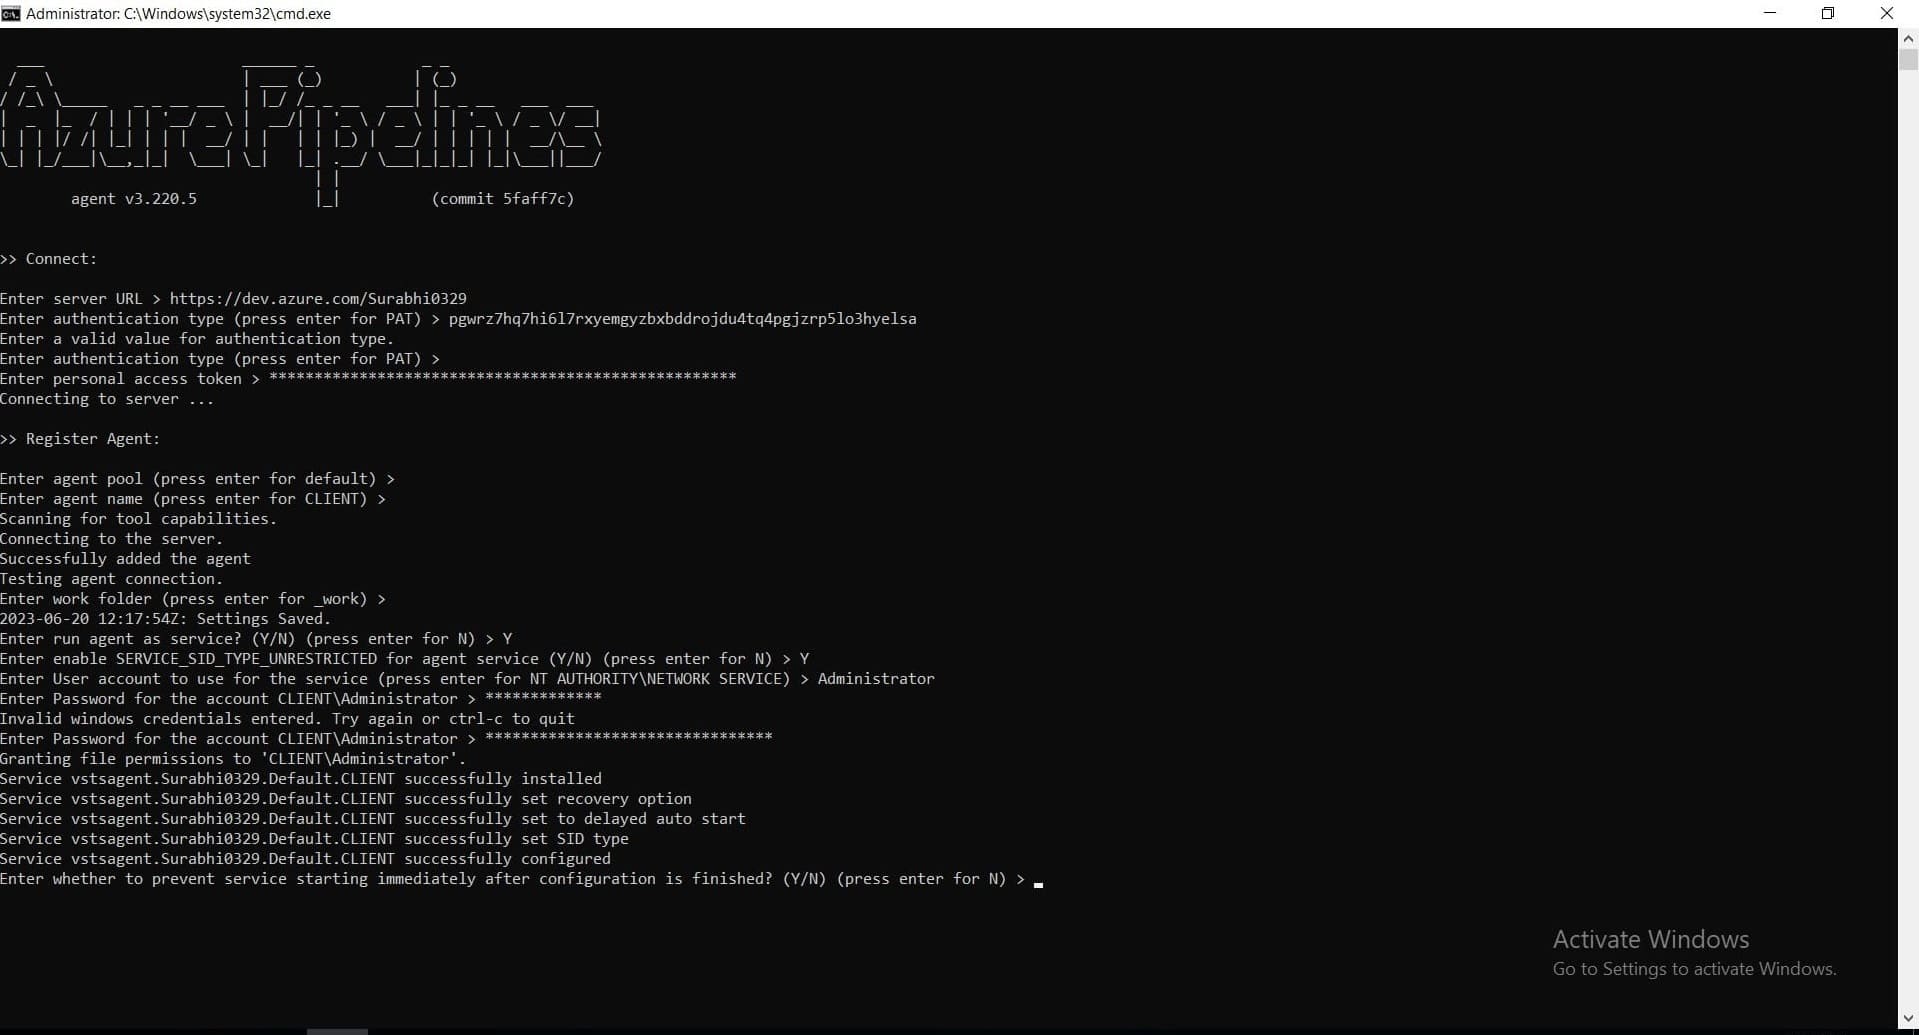
Now, Server url will be
https://dev.azure.com/<your_organization_name>
Just press enter for PAT on the authentication type and on the
next question provide the token copied earlier.
Once the Agent is registered, For Agent Pool, since we’ve it
as default, press enter If you want to name your agent
something you can name them but press enter for it to be named
as CLIENT.
Once the agent it added, You can leave the work folder as
default or change as per your choice For Running Agent as a
Service enter Y as in yes For User account to use for service
make sure you set this as Administrator, this is important because you’ll require Administrative
Privilege to perform code signing. Provide password for your
administrative account of your machine
Since we have set this as a service, the agent will run
automatically if we hadn’t set this as service, we would have
to manually run the agent.
Navigate to services.msc and scroll down to Azure Pipeline
Agent to see you’ve se Log on as Administrator. If you didn’t
do so, you can change it from itself. Just click on log on and
a dialogue box will appear; navigate to log on, set it to
Administrator and provide the password for the same and
restart the service. Once this is done, go back to Azure
DevOps to build the pipeline.
-
Click on pipelines to get started.
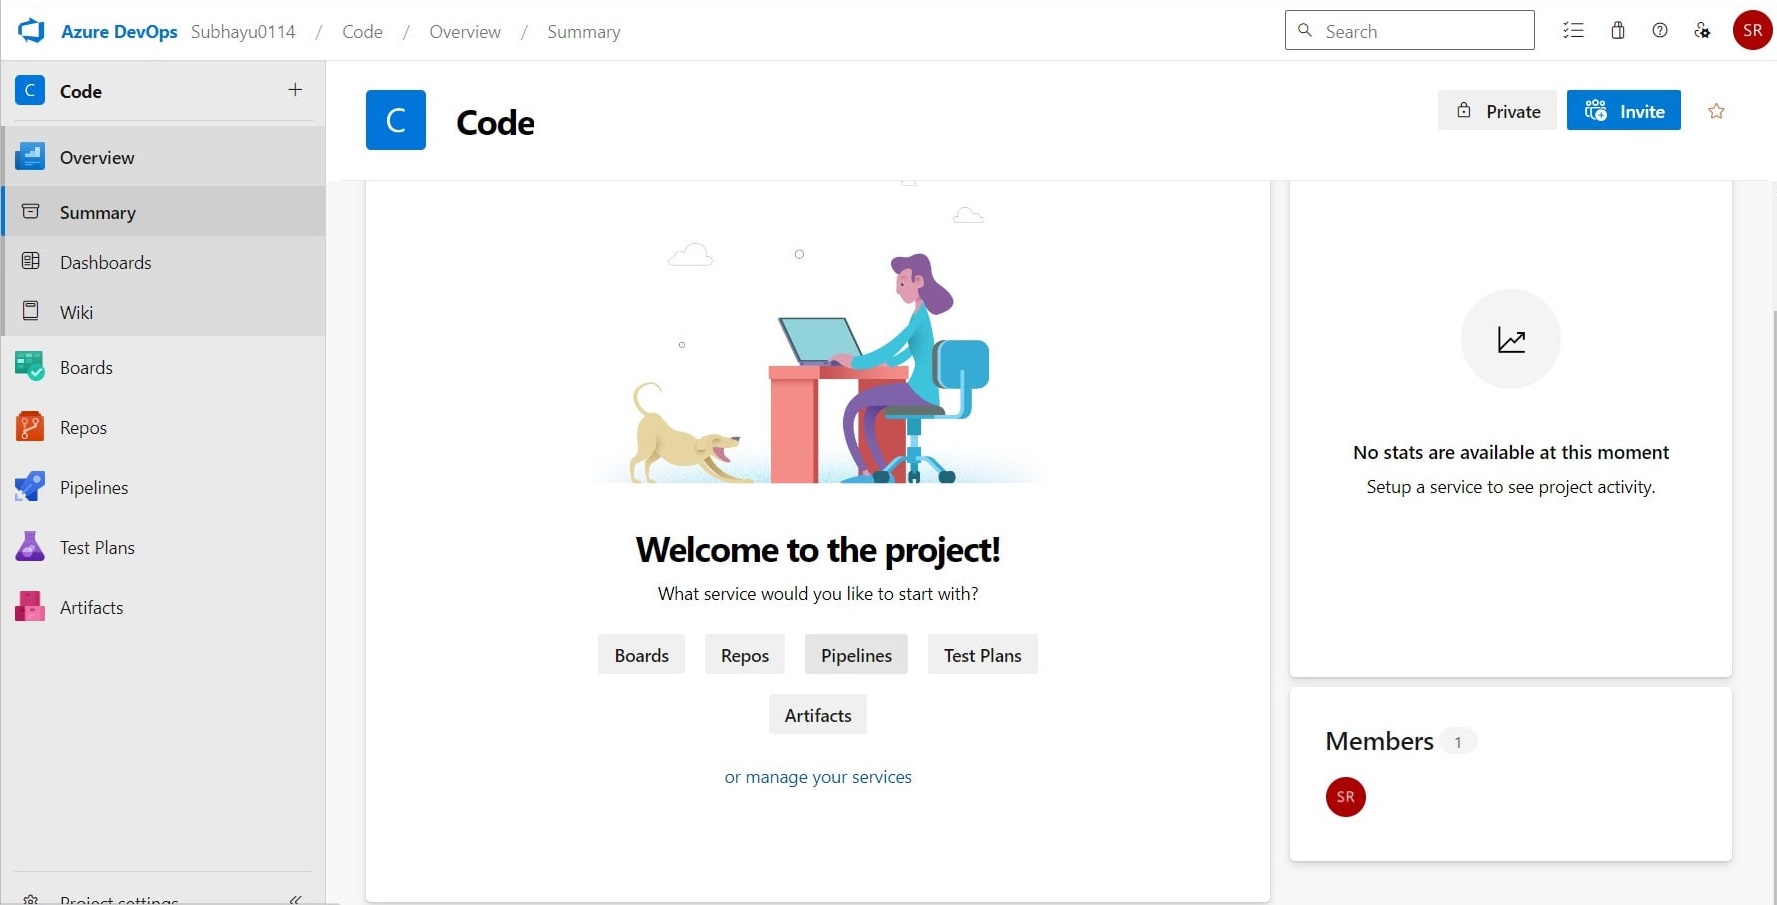
Click on Create Pipeline in the following page.
-
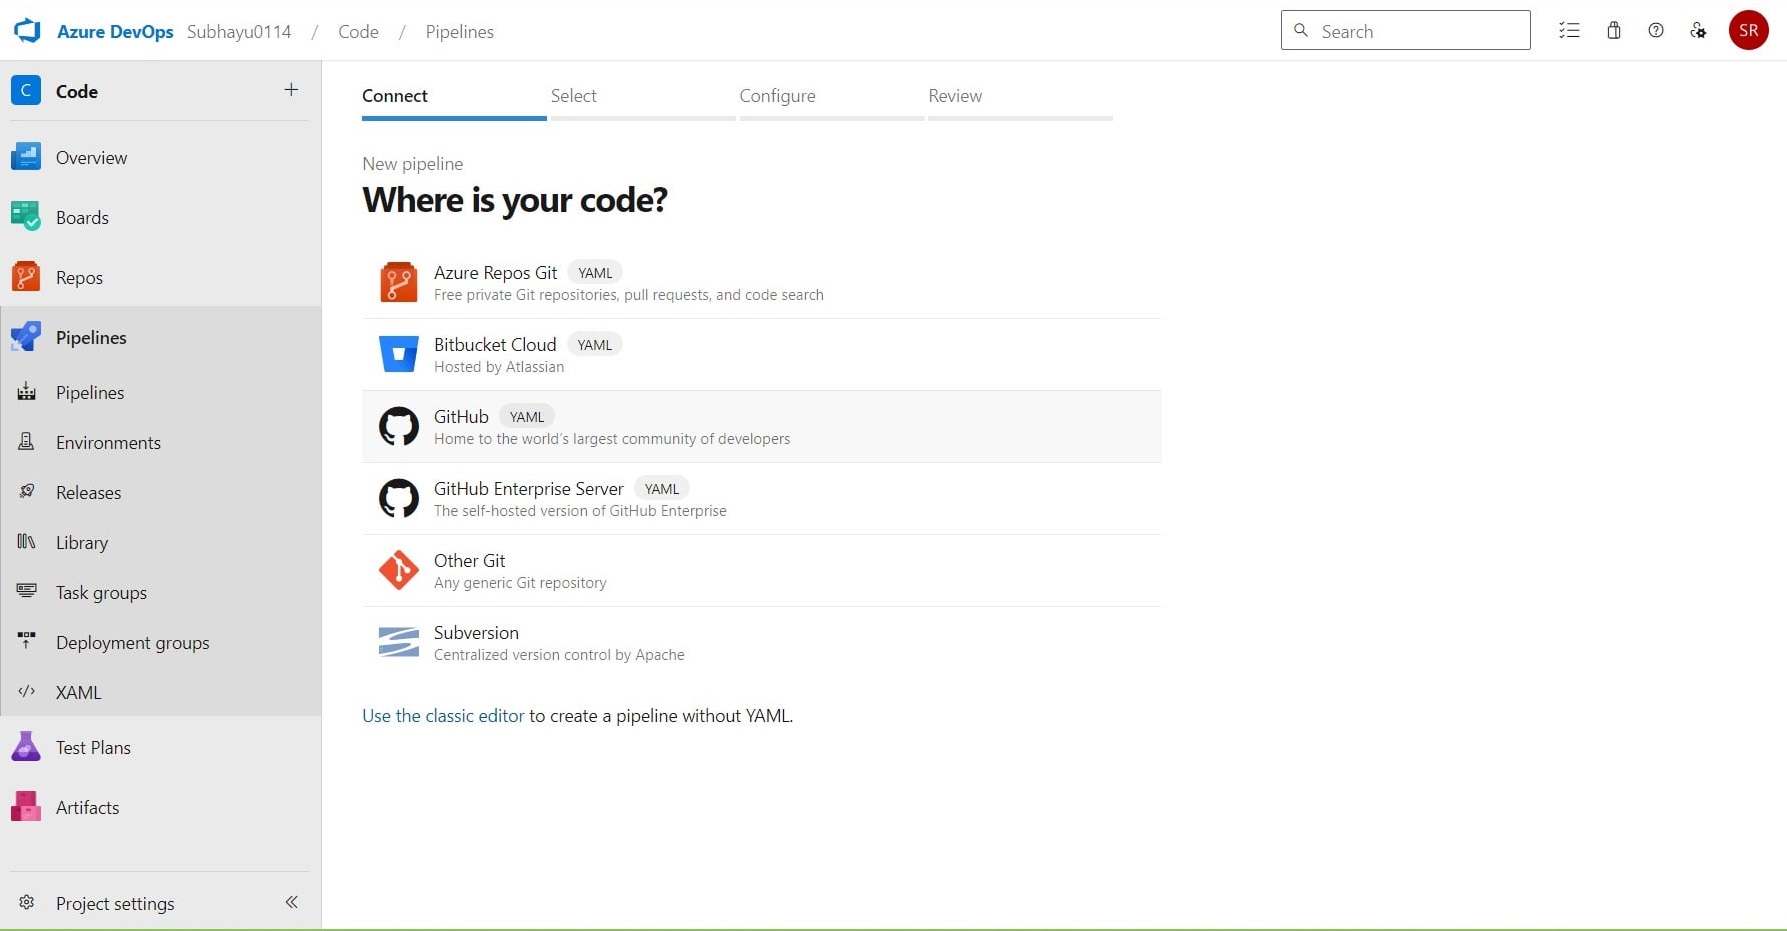
In the next page, in the Connect section, choose where your
code is. In this my code is in GitHub and I am proceeding with
so. You will require Administrative Privilege of your
repository to grant access.
-
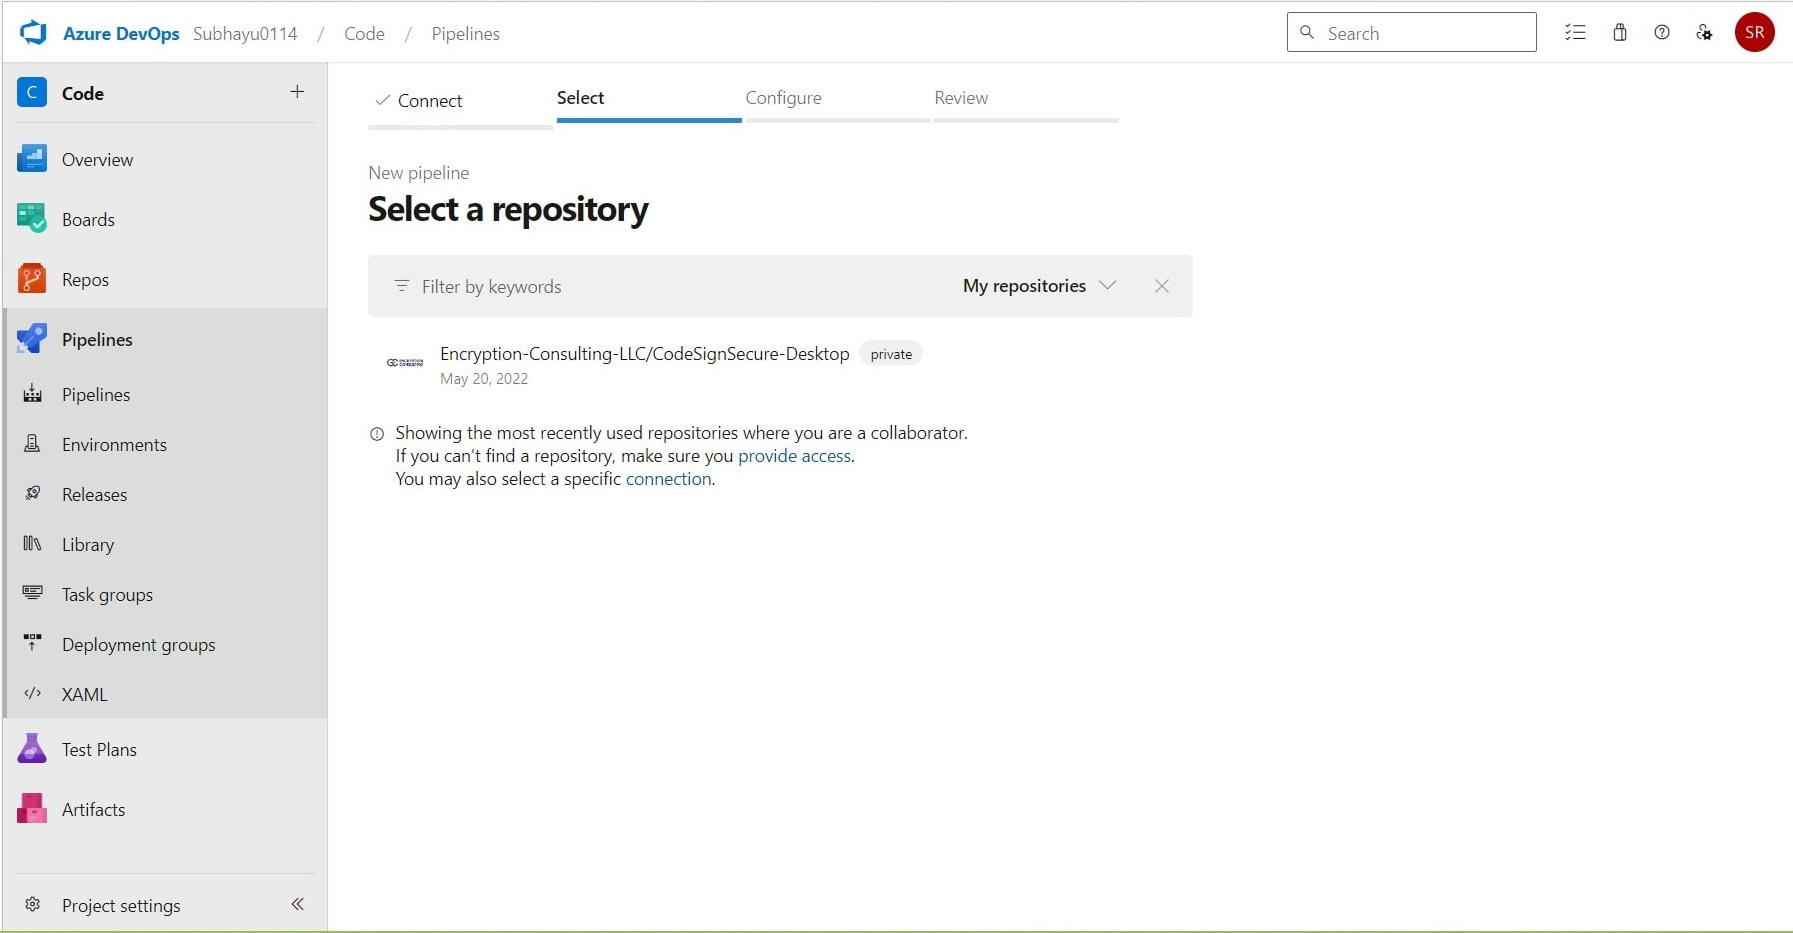
Select the repository where you’ve your code.
-
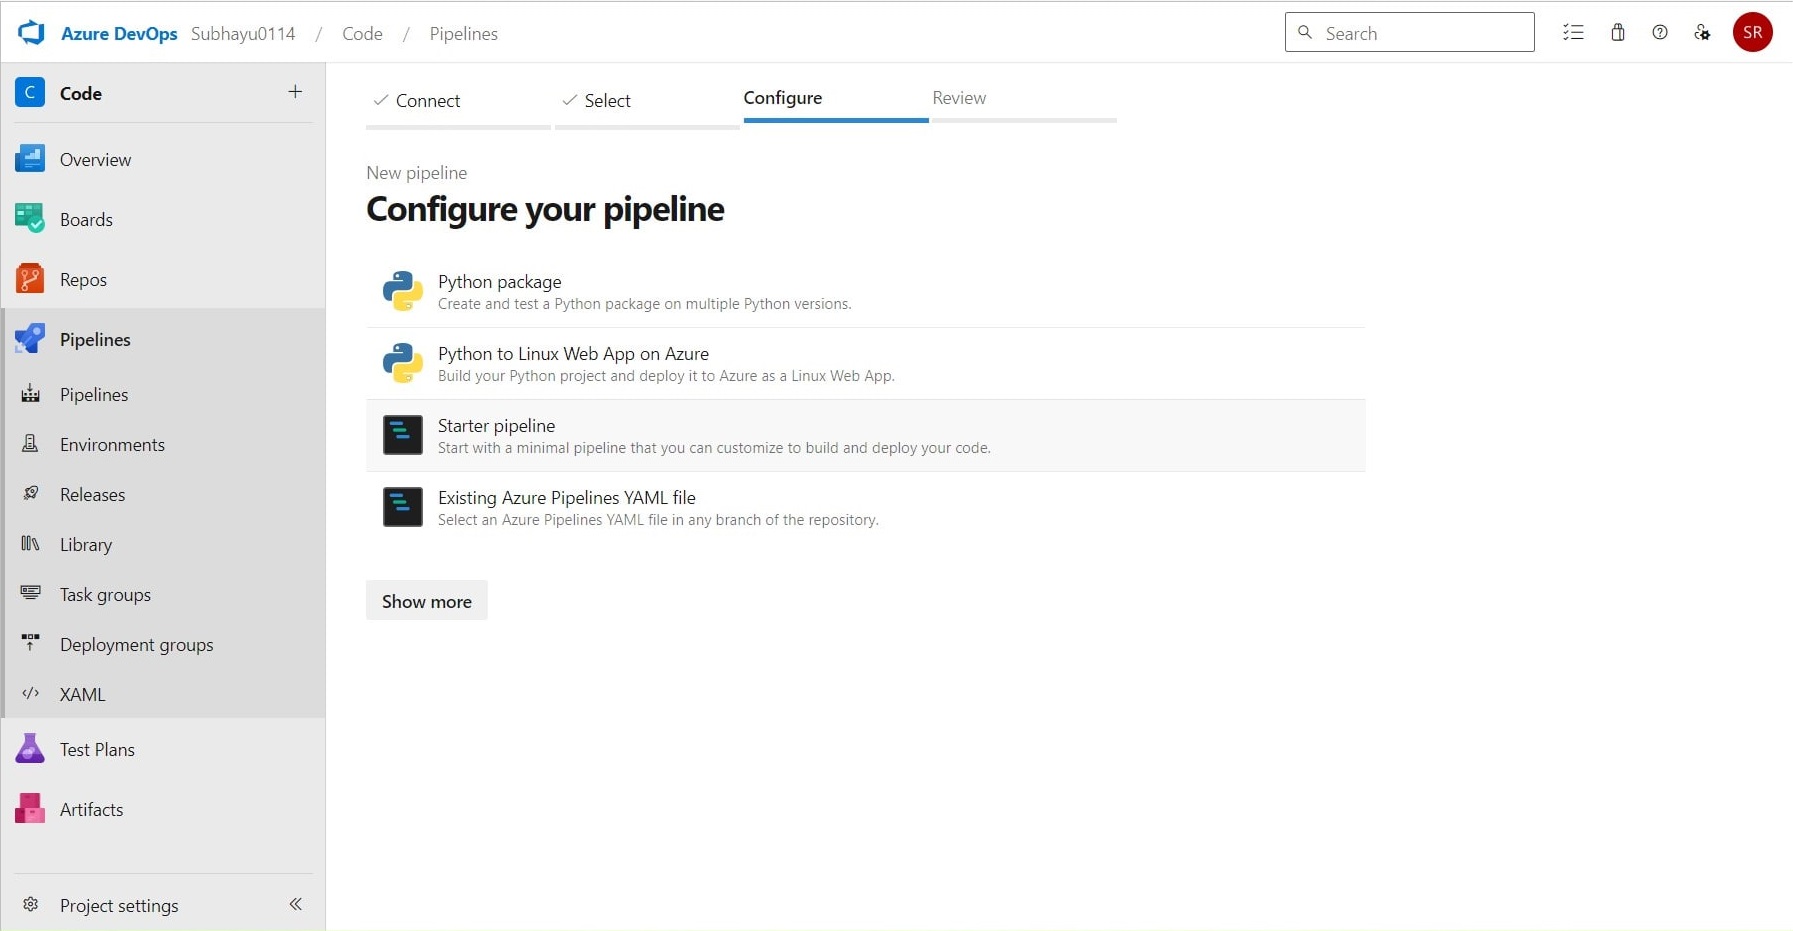
Now in the Configure Section, if you don’t already have .yml
file in your repository click on Starter Pipeline, if you do
click on Existing Azure Pipeline. For starter pipeline, you
may need to create a new branch or commit on the main branch
itself it’s your choice.
-
In the editor write the following script
                                    trigger:
                                    - <your_branch_name>


                                    pool:
                                      name: <your_pool_name> #In this documentation it’s set as Default


                                    variables:
                                      variable_name: variable_value


                                    steps:
                                      - script: |
                                          signtool sign /csp "Encryption Consulting Key Storage Provider" /kc <Key_name> /fd <hashing algorithm> /f <certificate location> /tr <time stamping server> /td SHA256 <file path>
Please replace the variables specified under
<variable name>. A
short description of expected variable is given below.
<key name>: This refers
to the cryptographic key used to sign the code. Example:
evcodesigning
<hashing algorithm>:
You need provide the name of hashing algorithm such as SHA256,
SHA384, or SHA512. It must be one of these three values.
<certificate location>:
An example of what can be put in this field is C:\testing.pem. The
certificate.pem file MUST be
included in this input. You can generate a pem file of the
certificate for codesigning, if you have the key name using,
ECSigningKSP. For doing so follow the commands below:
In your device where you have ECSigningKSP installed and
configured, navigate to the folder of ECSigningKSP, which is
usually present in “C:\Program Files\Encryption
Consulting\SigningKSP”
In your command prompt reach to this directory.
Then use following command to get pem file of the certificate
ECGetCert.exe <Key_Name>
(example: ECGetCert.exe evcodesigning)
Provide the location of the certificate saved.
<time stamp server>: A
timestamp server
provides proof that a digital signature was performed at a
specific time, allowing verification in the future that a file was signed at a
particular time. The one we generally use is
http://timestamp.digicert.com
<file path>: This is
where you provide the path of file that you want to sign. Example
C:\<Folder_name>\<File_name>. Make sure you have
provided a file name with the proper extension.
My script was
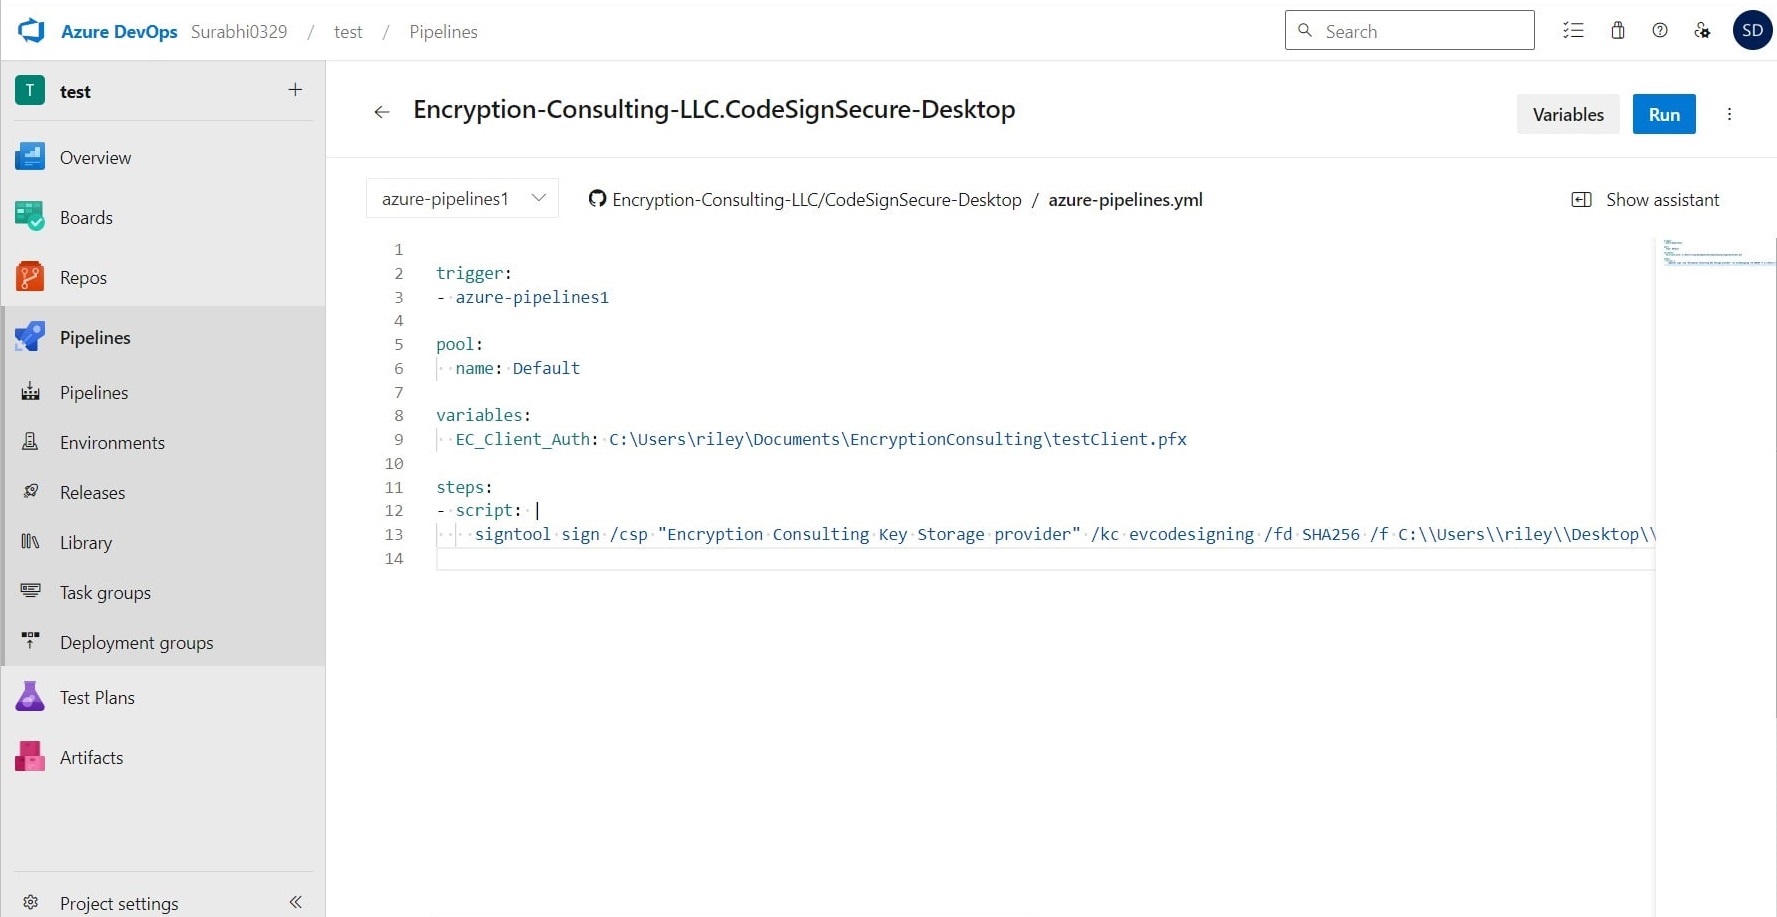
                                trigger:
                                - azure-pipelines1


                                pool:
                                  name: Default


                                variables:
                                  EC_Client_Auth: C:\Users\riley\Documents\EncryptionConsulting\testClient.pfx


                                steps:
                                  - script: |
                                      signtool sign /csp "Encryption Consulting Key Storage Provider" /kc evcodesigning /fd SHA256 /f C:\\Users\\Administrator\\Desktop\\ForTesting\\evcodesigning.pem /tr http://timestamp.digicert.com /td SHA256 C:\\Users\\Administrator\\Desktop\\ForTesting\\AgentService.exe
When you click save and run, you’ll prompted with branch tag, make
sure the name provided here and under trigger in script is same
before running the script.
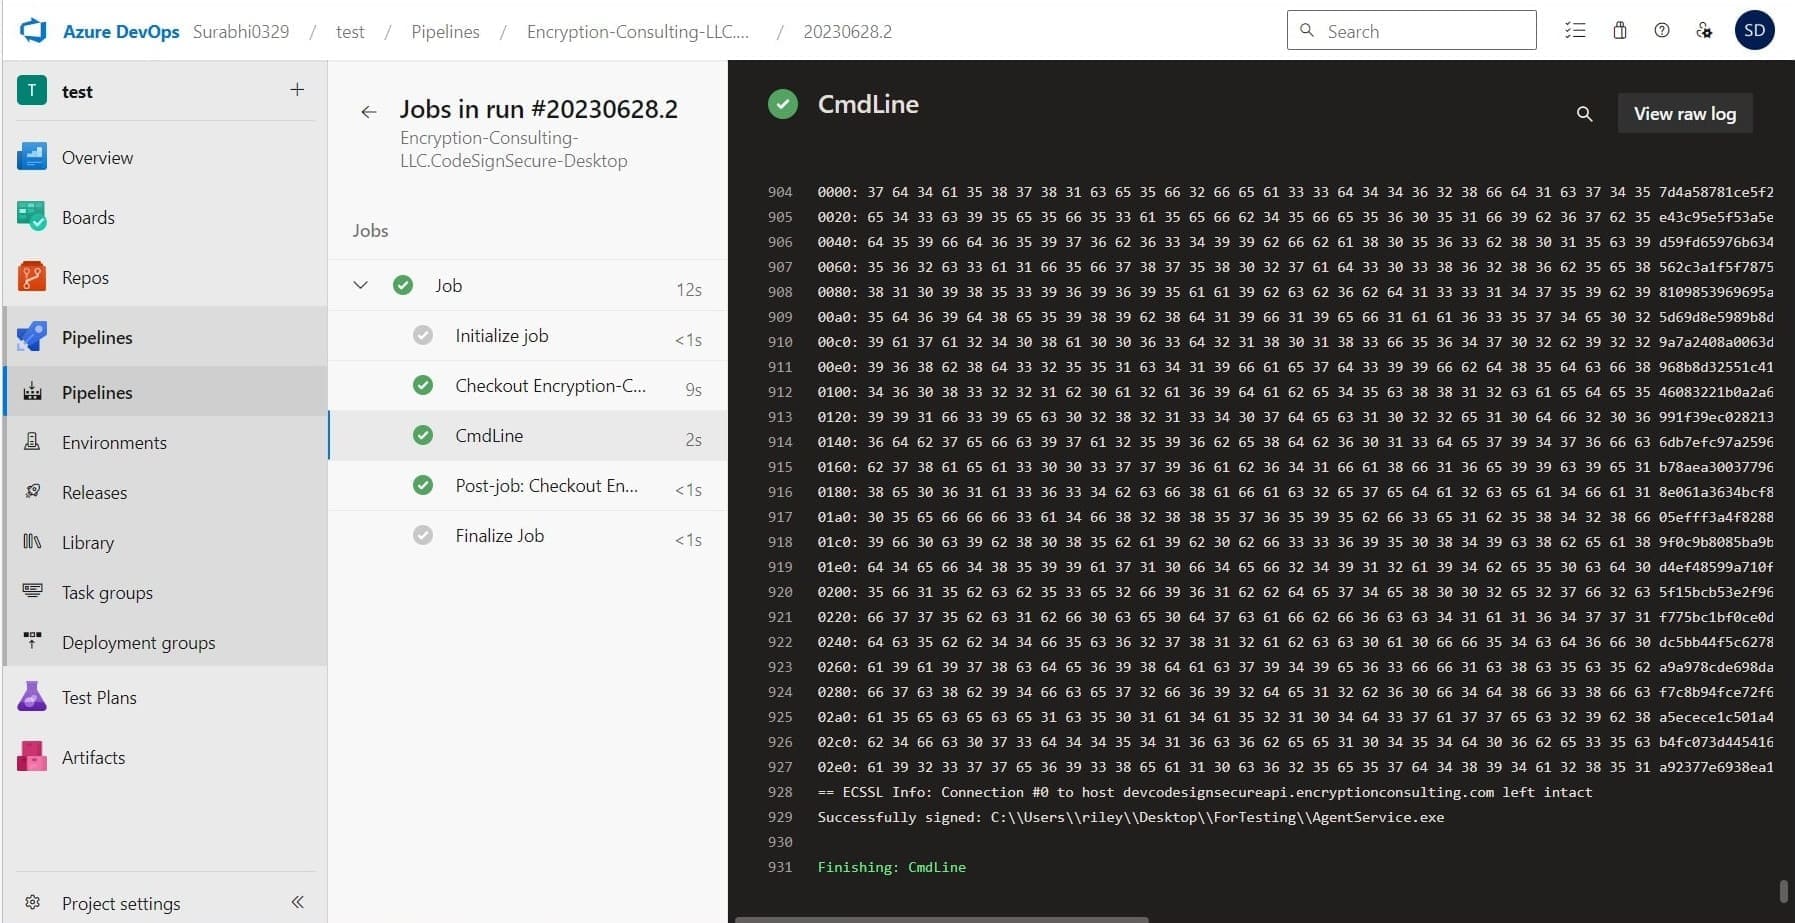
Once the build is successful, you’ll see that your file has been
successfully signed.