GitLab
Using Gitlab for code signing process require you to set up a
runner which has Signtool, ECSigningKSP and a GitLab Account.
Listing down the pre-requisites:
-
Self Hosted Runner which has ECSigning KSP, Signtool installed
and configured. This runner should be provided with
Administrative privileges.
- A GitLab Account.
To set up the ECSigningKSP and Signtool please navigate to the
Windows Signing page. After doing so, please follow the steps below:
To register a runner under Windows:
-
Run the following command:
.\gitlab-runner.exe register
-
Enter your GitLab instance URL (also known as the gitlab-ci
coordinator URL). Example:
https://gitlab.com
-
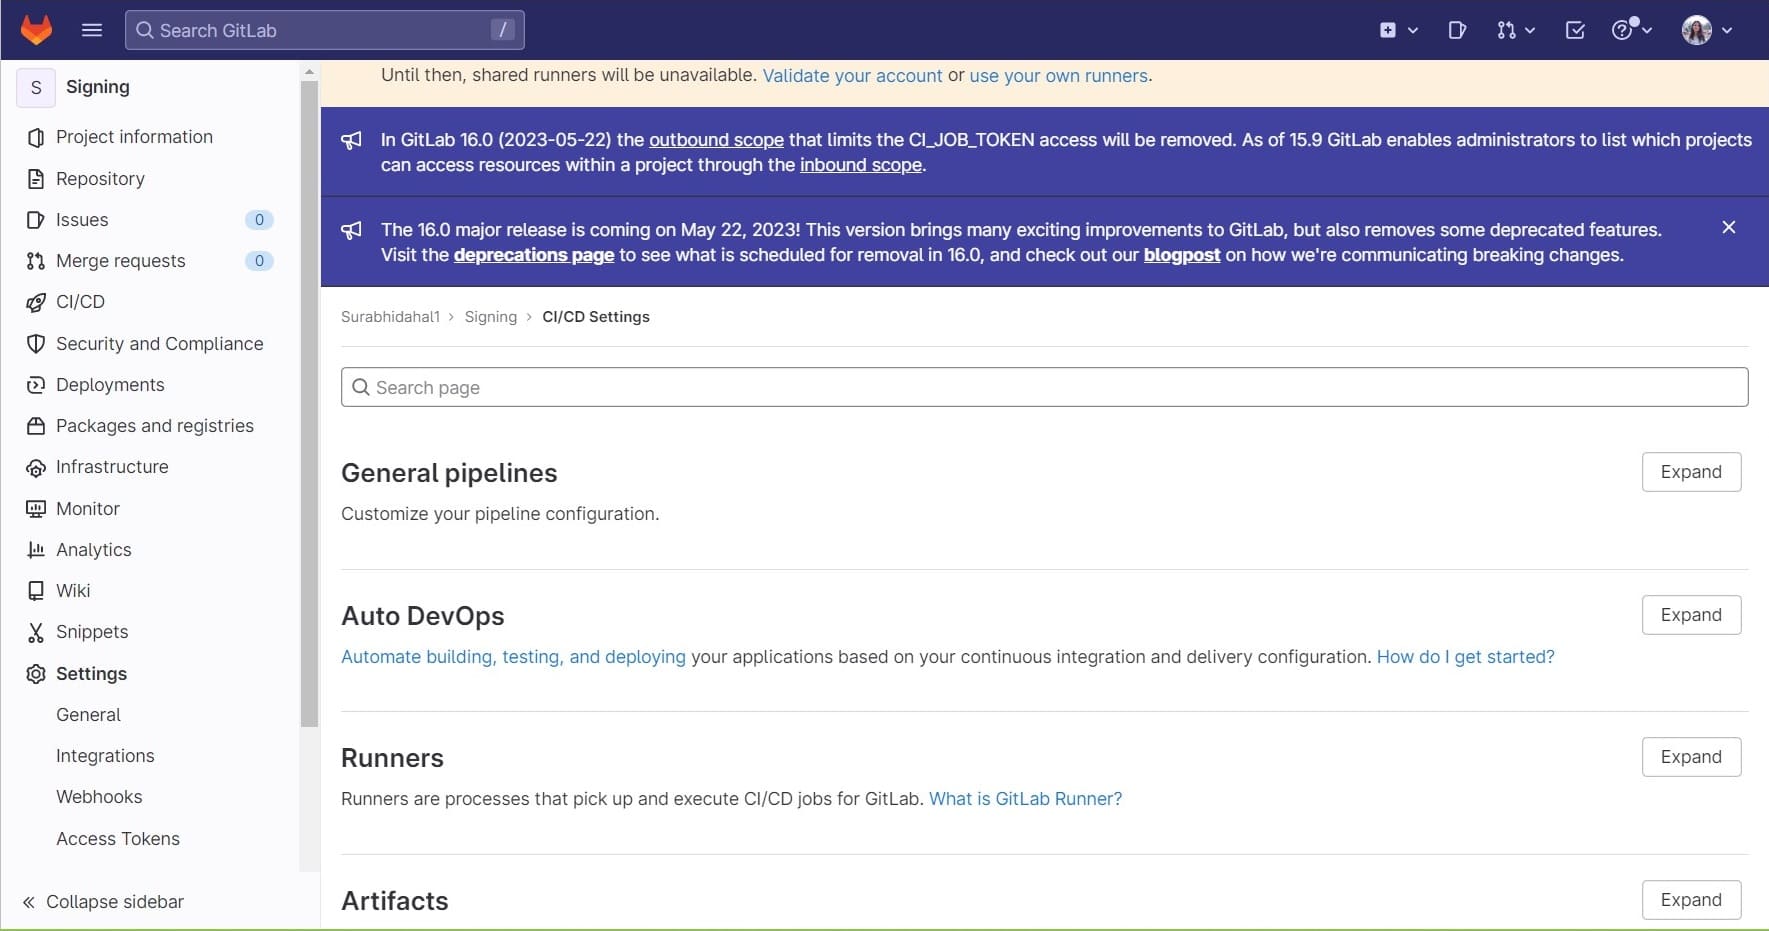
Enter the token you obtained to register the runner. You can
access this from settings -> CI/CD -> Expand -> Project runners.
Under project runners you can find token.
-
Enter a description for the runner. You can change this value
later in the GitLab user interface. Example: Device
-
Enter the
tags associated with the runner, separated by commas. You can change this value later in the
GitLab user interface. Example: WindowsRunner
- Enter any optional maintenance note for the runner.
-
Provide the
runner executor. We’re operating this in Shell.
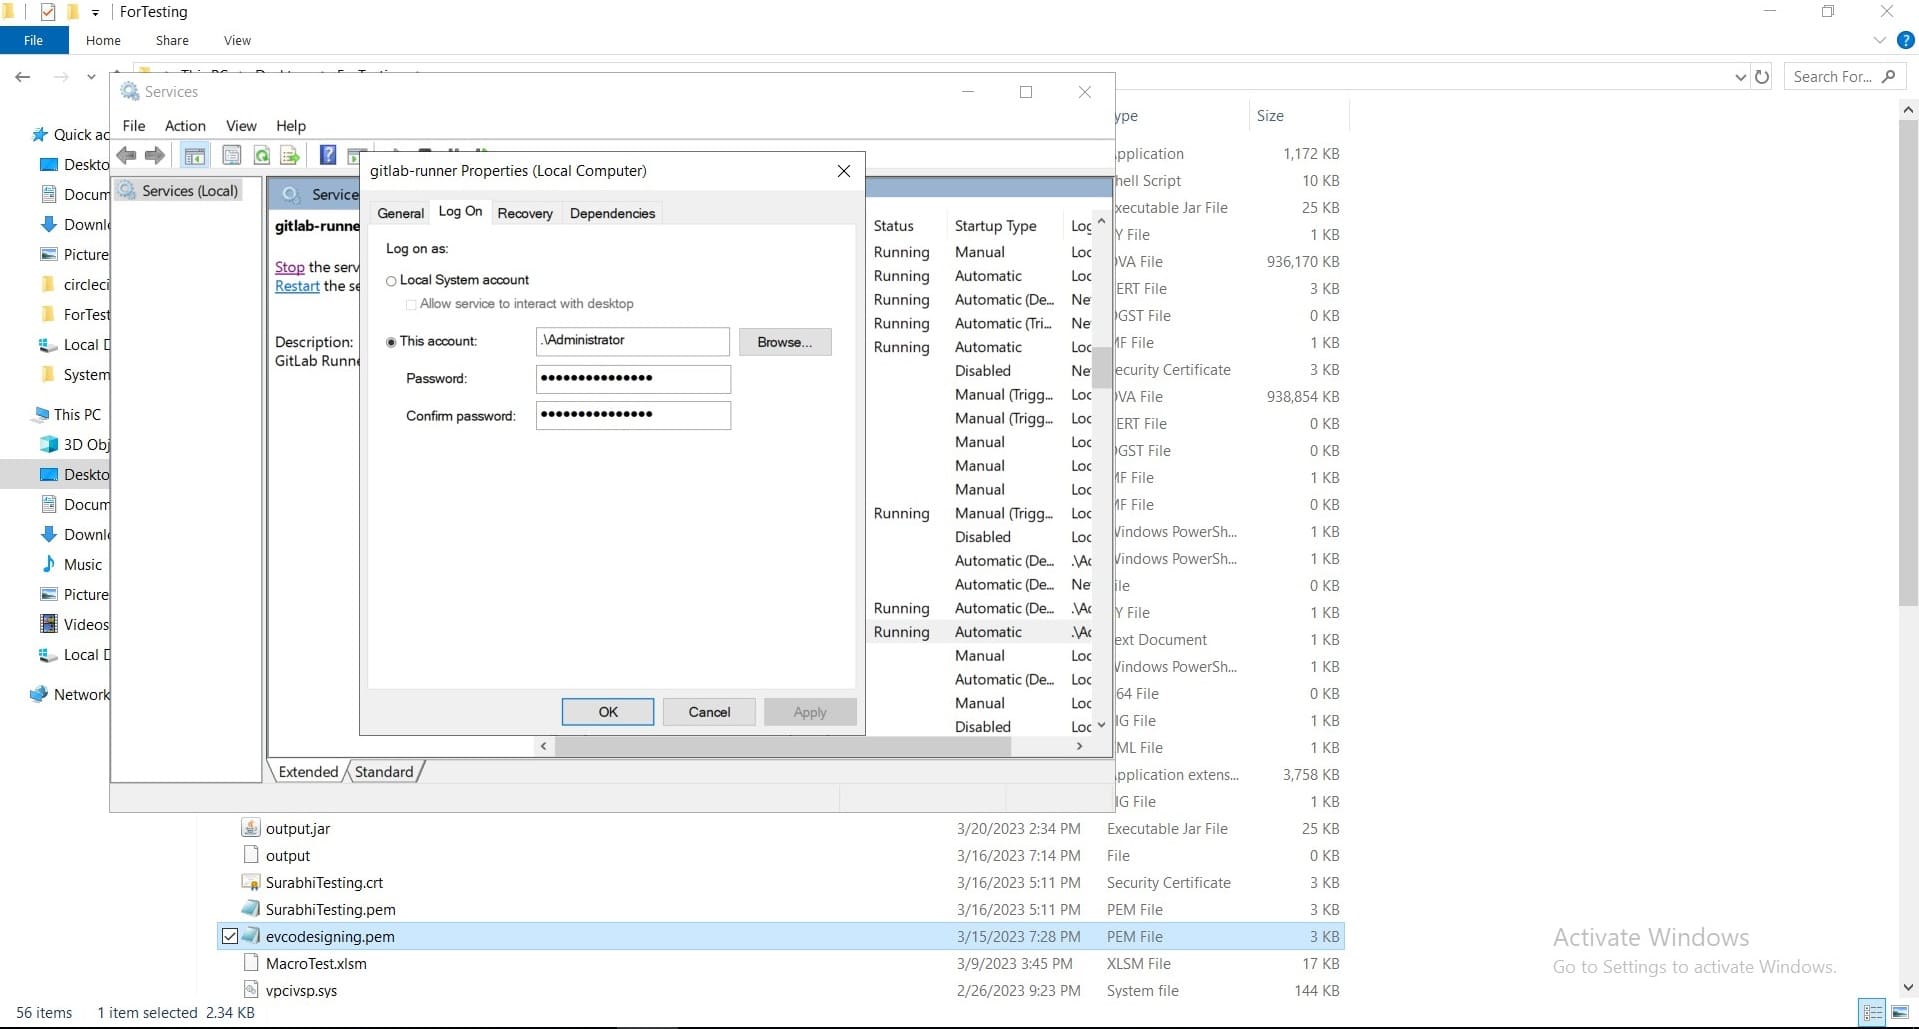
Once the runner is installed and configured, navigate to services
in your device, scroll down to GitLab Runner and set log on as
Administrator. Provide Admin Password here.
Once this is done, go to your project. You might have to rename
the .yml file name. Rename it as .gitlab-ci.yml.
There are three sections in this pipeline.
-
Tags
The tags you provided while setting up the runner
-
Variables
EC_Client_Auth :
Corresponds to the path of your SSL Authentication certificate
which can be created from CodeSignSecure.
EC_Client_Pass :
Corresponds to the password of your certificate which is
provided at the time of creation of the certificate.
-
Script
Provide the signtool command to sign a file.
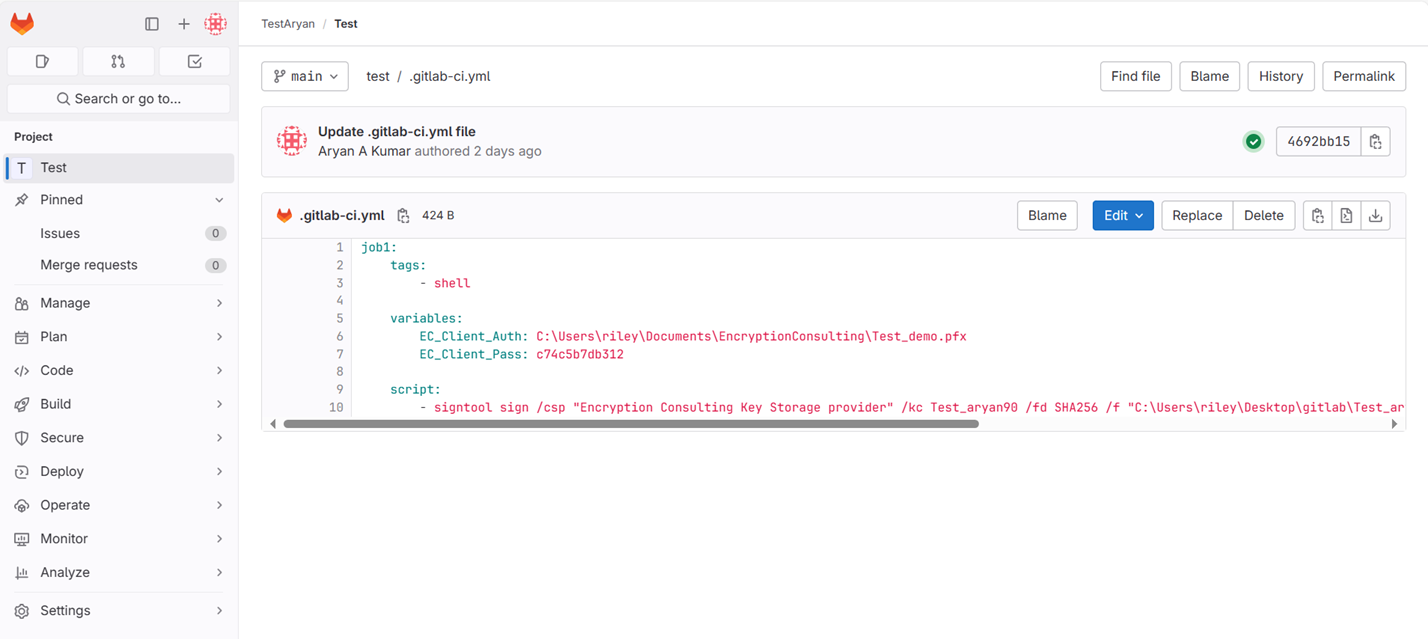
A sample script is given below to perform codesigning.
                                    job1:
                                            tags:
                                                    - shell

                                            variables:
                                                    EC_Client_Auth: C:\Users\riley\Documents\EncryptionConsulting\Test_demo.pfx
                                                    EC_Client_Pass: c74c5b7db312

                                            script:
                                                    - signtool sign /csp "Encryption Consulting Key Storage Provider" /kc Test_aryan90 /fd SHA256 /f "C:\Users\riley\Desktop\gitlab\Test_aryan90.pem" /tr http://timestamp.digicert.com /td SHA256 "C:\Users\riley\Desktop\agent.exe"
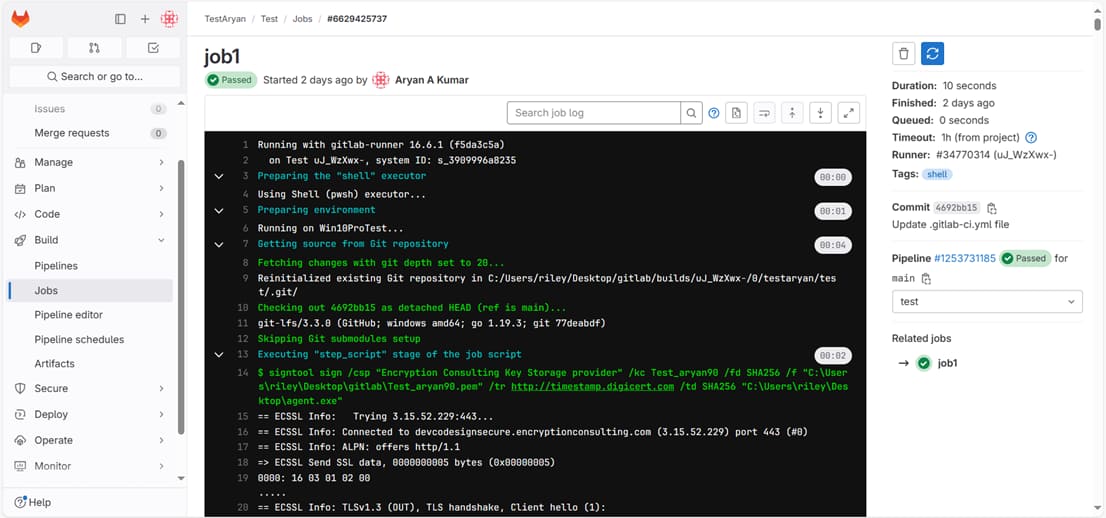
If you click on Build -> Jobs, you'll see it being
successfully signed.
You'll need to modify the command as per your variables
-
kc <certificate name>: replace Test_aryan90 with your key name
-
f <certificate location>: replace location with location of your certificate .pem file to perform
codesigning.
-
tr http://timestamp.digicert.com: time stamping server
-
td SHA256 <file location>: location of file you want to get signed.