
Activity 2: Publish EC CA Certificates to NTAuth
The NTAuth store in Active Directory lists the CAs that Windows trusts to issue certificates for authentication. Because the Issuing CA is in the EC network, its certificates must be added to NTAuth by hand. Domain-joined computers then receive them automatically through Group Policy.
- Copy the Root CA and Issuing CA certificates supplied by EC to
C:\Certson the Domain Controller. - Open Command Prompt as Administrator and publish the certificates:
certutil -dspublish -f "C:\Certs\EC-RootCA.cer" NTAuthCA
certutil -dspublish -f "C:\Certs\EC-RootCA.cer" RootCA
certutil -dspublish -f "C:\Certs\EC-IssuingCA.cer" NTAuthCA
certutil -dspublish -f "C:\Certs\EC-IssuingCA.cer" SubCA
Each command ends with Certificate added to DS store and CertUtil: -dspublish command completed successfully.
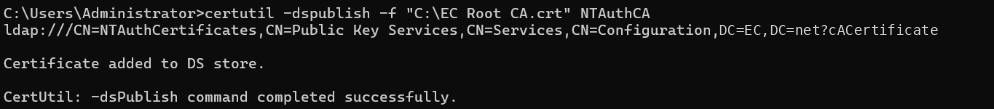
- Check the result:
certutil -viewstore "ldap:///CN=NTAuthCertificates,CN=Public Key Services,CN=Services,CN=Configuration,DC=example,DC=com"
