
- Overview
- Reference Guide
- Setup & Architecture
- Release Notes
- Workflow
- API Reference
- Integration Guide
- Discovery Agent Setup Guide
This section lets you generate and monitor API tokens, which enables seamless integration with other systems and services. Through the API, you can programmatically interact with key functionalities such as certificate management, reporting, and configuration settings, helping automate workflows and improve interoperability with other tools in your organization.
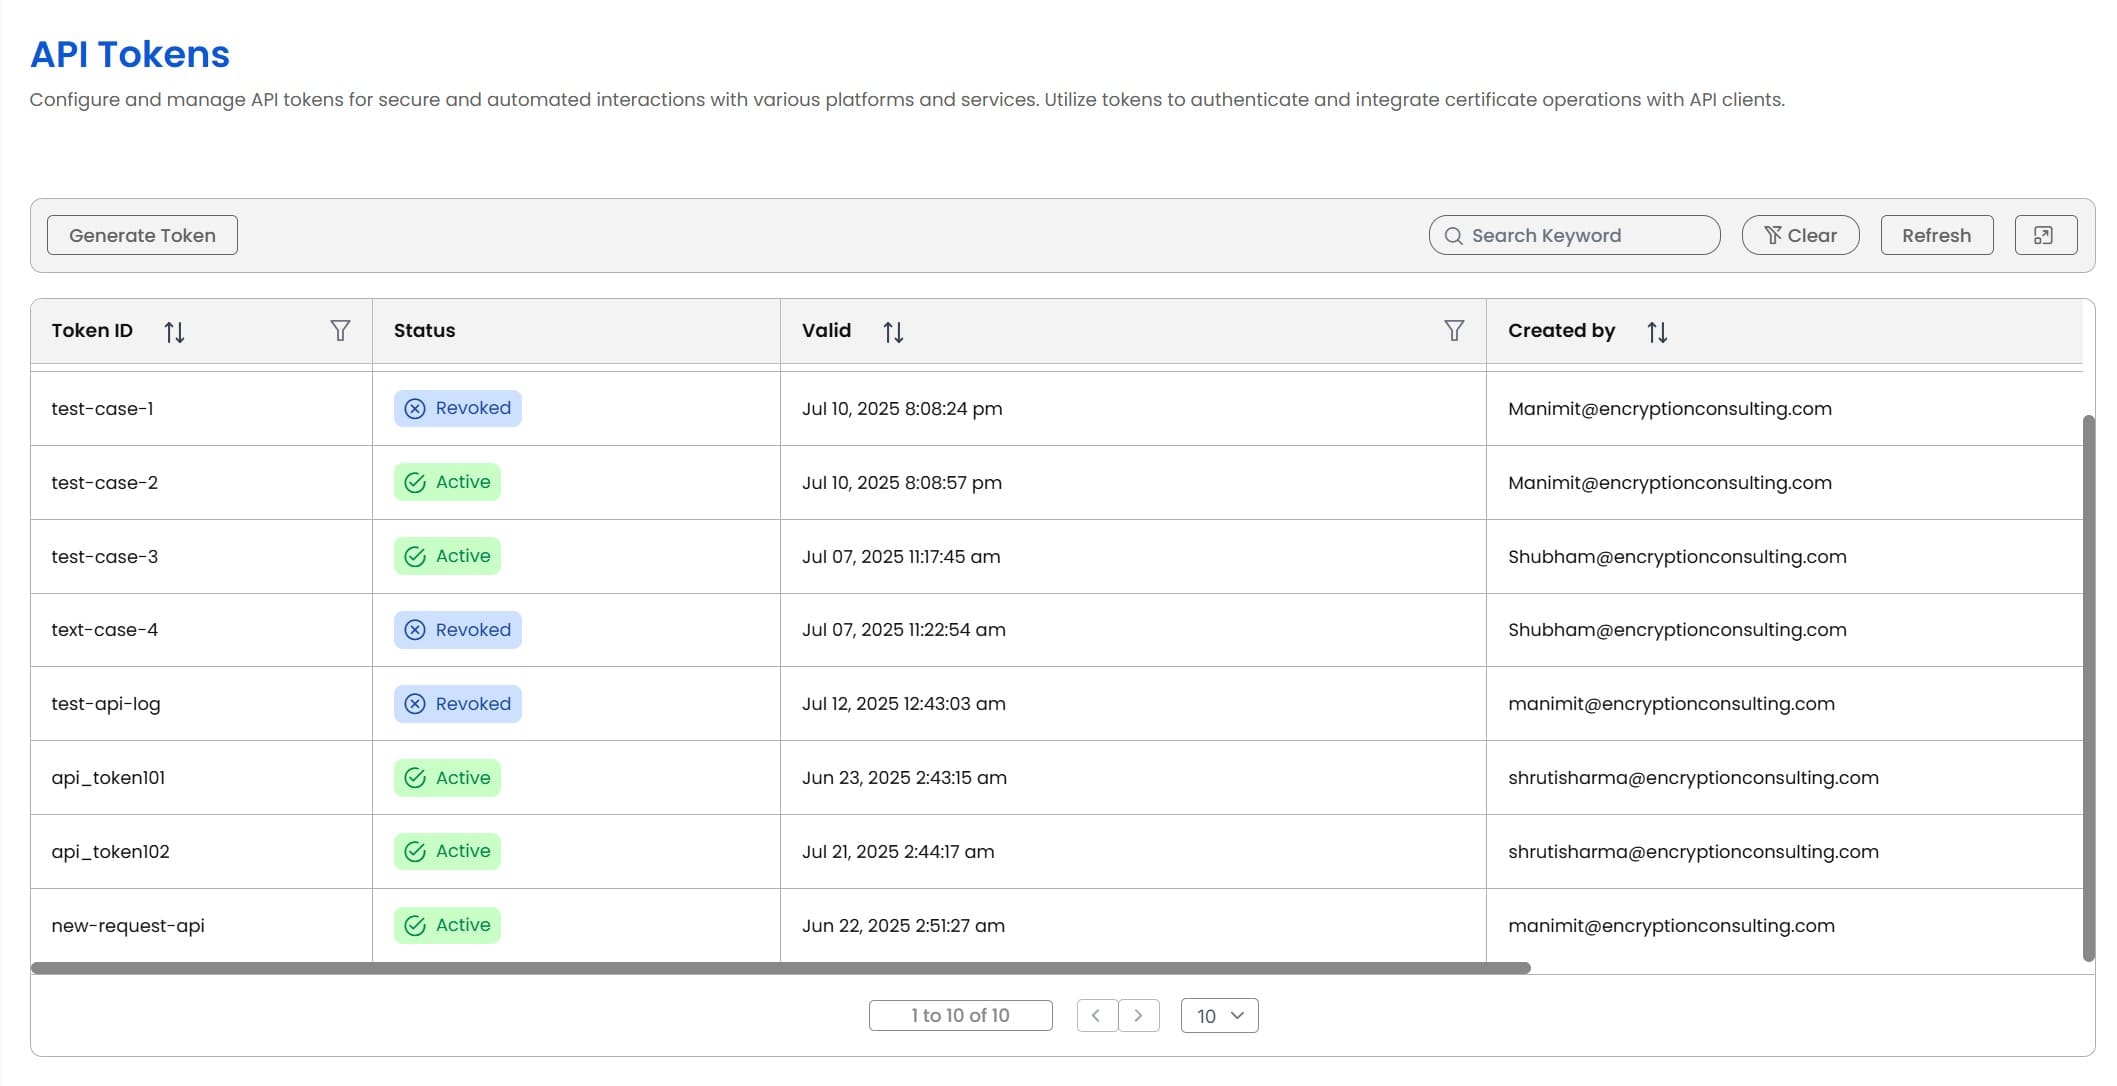
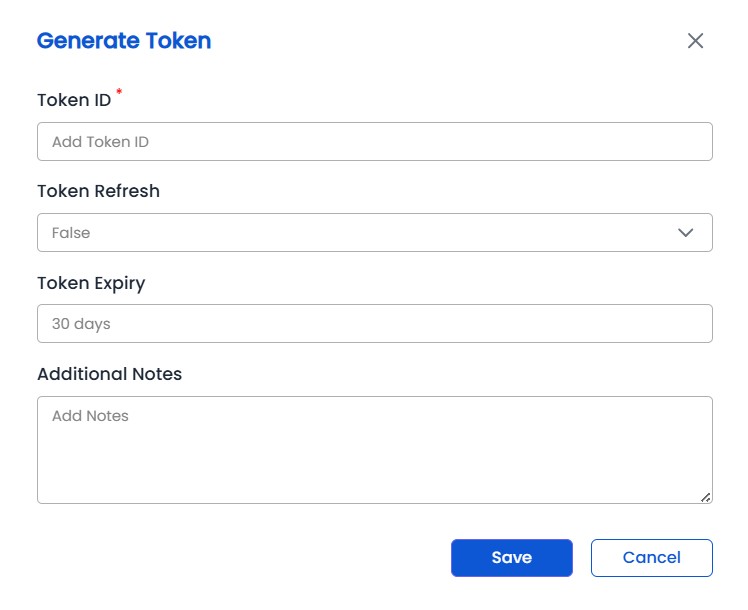
API tokens with Token Refresh parameter set to true, allows renewal of API token. API tokens with Token Refresh parameter set to false are one-time tokens which expire after Token Expiry period or validity in days.
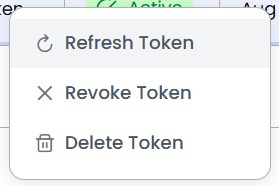
An User with with Manage API Tokens permissions can create, renew, revoke, delete their API tokens. Admin Roles (e.g., Admin, PKI Admin, Department PKI Admin) can renew, revoke, or delete any available tokens in the environment, based role-based access.
Role-Based Access on API tokens visibility:
Note: Access to this section is provided by the `Manage API Tokens` Permission in Roles